Claude Code v2.1.270 to v2.1.272 Key Updates - Sub-agent omitClaudeMd and permission-related fixes

This page has been translated by machine translation. View original
This is Ishikawa from the Cloud Business Division. I'd like to summarize the Claude Code updates for v2.1.270 ~ v2.1.272 (2026-09-12 ~ 2026-09-14). There are many permission-related changes, and I feel it's worth checking for those who have carefully configured their settings. Today, I tried out omitClaudeMd, which allows specified sub-agents to skip reading CLAUDE.md.
The previous update article is here.
Update Summary
This covers 3 versions (v2.1.270 ~ v2.1.272, 2026-09-12 ~ 2026-09-14). The CHANGELOG lists 98 changes, with 96 of them concentrated in v2.1.271. The breakdown shows bug fixes accounting for about half, followed by improvements to existing features, and then permission/security-related changes (the classifications and counts are as organized in this article). v2.1.272 only states "Bug fixes and reliability improvements" with no individual items listed.
Notable Updates
4 Bash Permission Check Gaps Fixed (v2.1.271)
The following 4 issues were fixed regarding Bash permission checks.
- Files read by commands like
fmtorcolumnbeing missed when they appear after options unknown to the checker - Files that wildcard expansion targets being skipped when wildcards are in command pattern positions or option value positions (e.g.,
grep -v dir/* file) - Shell variable declaration flags being used to misrepresent which commands are executed
- Commands containing two directory changes, subshells, or
cdandgitconcatenations skippingpermissions.blockReadsOutsideWorkingDirectorieschecks in bypass mode and auto mode
I feel that the more carefully you've written permission rules and the more you rely on auto mode or bypass mode, the more likely it is that commands that previously passed without prompting will now require confirmation.
Per-Command allowed_domains Added to Auto Mode (v2.1.271)
In auto mode with sandbox enabled, per-command allowed_domains has been added to Bash, PowerShell, and Monitor. The hosts required by a command are checked together with that command and opened only for that specific command. Other hosts are denied.
For those who handle network-using commands under sandbox, I feel the ability to narrow permission scope down to the per-command level will make a real difference.
Handling of Inline ! Commands in Auto Mode Changed (v2.1.271)
Inline ! shell commands written in skills or slash commands now follow default mode permission rules instead of the classifier. Commands not resolved by any rule are executed as tool calls subject to review.
For those who write ! shell commands in skills or slash commands, how they pass in auto mode will change, so I recommend cross-checking against your own permission rules.
Sub-Agent omitClaudeMd (v2.1.271)
omitClaudeMd has been added to agent front matter and --agents JSON. Custom sub-agents and plugin sub-agents can now run without reading user, project, or local CLAUDE.md files. Managed policy files continue to be read.
For those with sub-agents where you don't want the repository's CLAUDE.md applied, I feel this becomes a way to separate the scope of instruction application.
--accept-command for plugin install / update (v2.1.271)
--accept-command <sha256> has been added to claude plugin install and claude plugin update. Instead of -y, you specify approval by providing the sha256 of the command matching what the preceding --json run displayed.
For those who install or update plugins from CI, I feel the ability to narrow approval to a single command will be useful.
Fixed Double-Launch of Background Commands After Compact (v2.1.271)
An issue has been fixed where Claude would launch background commands (such as watch tasks or development servers) that were still running again after compacting a conversation.
For those who run long conversations while keeping a development server running, I feel this will reduce hard-to-diagnose failures like port conflicts.
Fixed File Read Tracking for /resume and /teleport (v2.1.271)
An issue has been fixed where /resume and /teleport would carry over file read tracking from previous conversations, allowing Claude to edit files that had never been read in the resumed conversation.
For those who resume conversations to continue work, I feel this will be effective in preventing unintended edits.
Fixed Permission Prompts for Read-Only Git Commands (v2.1.270)
An issue where read-only Bash git commands would suddenly start requesting permissions after a session had been running for a while has been fixed. This was a regression introduced in v2.1.269.
Since this issue was more likely to be encountered the longer the session ran, I feel it's worth upgrading if you're on v2.1.269.
Target Versions and Period
| Version | Release Date | CHANGELOG Entry Count |
|---|---|---|
| v2.1.270 | 2026-09-12 | 1 |
| v2.1.271 | 2026-09-14 | 96 |
| v2.1.272 | 2026-09-14 | 1 (no individual items listed) |
New Features
New features beyond the allowed_domains, omitClaudeMd, and --accept-command covered in the notable updates section are as follows.
- Fast mode is now available for Claude Code Remote sessions (cloud and self-hosted runners). Host-side settings or
/fastwithin a session are applied within the scope permitted by the organization (v2.1.271) - The full-screen
/configpanel now supports mouse operation. Scroll with wheel, click to change values, and pointer row highlighting are available (v2.1.271) - Added
claude self-hosted-runner --drain-marker-file <path>. When that file is present during a SIGTERM drain, the runner reports its own termination as a host drain (telemetry only) (v2.1.271) - Managed setting
modelPricingand Claude apps gatewaypricingblock now supportmultipliervalues greater than 1 (up to 10). You can configure a markup rate for internal chargeback (v2.1.271) - Added spinner hints directing Bedrock, Vertex AI, Foundry, and LLM Gateway users to the Claude desktop app. The claude.ai desktop app hint directs to
/desktop(v2.1.271) - [VSCode] Added Attach Open File setting. When turned off, the currently open file will not be attached (selected text will still be attached) (v2.1.271)
- [Claude Code on the web] Added Custom network access option to the Cloud environments editor in management settings (v2.1.271)
Improvements
- Improved terminal rendering performance. Rendering large diffs and long transcripts is faster, with fewer slow frames (v2.1.271)
- Eliminated duplicate validation of built-in model data, slightly improving startup time (v2.1.271)
- Dynamic workflows now pause rather than terminate the relevant agent at usage limits, and automatically continue after reset (v2.1.271)
- The default size for dynamic workflows has changed to small for Pro plans, and the target size for medium has changed from 15 agents to 10 agents (v2.1.271)
- While hooks are running, the spinner now shows this status and elapsed time, and prompts waiting for SessionStart hooks can be cancelled with Esc (v2.1.271)
- In auto mode, sub-agents now report back to the caller via a dedicated handback call subject to safety classifier review (v2.1.271)
- With
claude mcp serve, running tool calls now send progress every 30 seconds, preventing long commands without output from being interrupted by idle timeout (v2.1.271) - For Foundry and Claude Platform on AWS sessions,
alwaysLoadMCP servers that complete connection mid-conversation are now available from the next turn (v2.1.271) - Markdown files published as artifacts now render as document pages with title headers and syntax highlighting (v2.1.271)
- The number of published artifacts a single session can monitor for republishing has increased from 5 to 10 (v2.1.271)
- The IDE selection indicator in the prompt is now displayed as a
[⧉ …]pill, wrapping with text without crowding multi-line prompts. Pressing Backspace removes it from the submission target (v2.1.271) - Claude apps gateway, Bedrock, Vertex AI, and Foundry sessions no longer refresh claude.ai logins that aren't used in that session (v2.1.271)
Fixes (Major)
Excerpting fixes primarily related to stability and usability.
- Fixed issue where old organization policy is used after account switch: The cache was reused after switching and not refreshed until the hourly check (v2.1.271)
- Fixed tool list not updating after organization policy is applied: The tool list and command list were not updated when loading completed after startup or when changes occurred during a session (v2.1.271)
- Fixed issue where unreadable managed-mcp.json was silently ignored: It now warns at startup while maintaining exclusive MCP control (v2.1.271)
- Fixed MCP OAuth client registration handling: Issues included forced re-registration on consent denial, reuse of registrations for different redirect URIs, and registration loss due to concurrent writes (v2.1.271)
- Fixed high CPU usage from MCP server notification loop: Occurred when a server kept sending
list_changedat short intervals (v2.1.271) - Fixed 1M context being dropped with
--resume: Occurred when the model family of the resumed session differed from the default model (v2.1.271) - Fixed artifacts disappearing after
--resume: Items attached with/artifactswere disappearing from the session (v2.1.271) - Fixed
claude -presume failing for sessions with only MCP tools (v2.1.271) - Fixed turns failing on LLM gateway responses: Occurred when non-streaming responses were returned as
text/plain(v2.1.271) - Fixed reduced display count for
/resumeand/continue: Only 1–2 items were displayed in full-screen mode on short terminals (v2.1.271) - Fixed git operations breaking after sandbox failure (Linux): An old
.git/config.lockwas being left behind (v2.1.271) - Fixed config file changes not being detected (macOS): On machines where the file event service is saturated, the watcher falls back to polling (v2.1.271)
- Fixed skills persisting after sign-out: Copies not updated within
cleanupPeriodDaysare moved to trash (v2.1.271) - Fixed self-hosted runner losing host configuration: Occurred when the configuration directory exceeded 64 MiB. Also added
--host-config-snapshot disk|memory(v2.1.271) - Fixed PowerShell commands failing without output on Windows: Occurred when the temporary output path reached 260 characters (v2.1.271)
- [VSCode] Fixed Hooks dialog saving: Issues included successful saves being reported as failures and hooks being duplicated on replacement (v2.1.271)
- [VSCode] Fixed console window flickering on Windows (v2.1.271)
- [VSCode] Fixed new chat reverting to previous chat (v2.1.271)
- [Claude Code on the web] Fixed cloud session responses freezing for about 10 minutes (v2.1.271)
- [Claude Tag] Fixed loss of work context in thread-centric channels (v2.1.271)
- [Claude Tag] Fixed inability to receive PR CI failures and reviews after restart (v2.1.271)
- [Code Review] Fixed missed reviews and duplicate posts: Issues included missed commits arriving while awaiting review, the same finding being posted multiple times, and resolved security findings being reposted (v2.1.271)
- A quietly welcome fix: Fixed an issue where terminal capability query responses (
^[[?1;2c) would appear in the shell prompt or editor on exit, suspend, etc. (v2.1.271). For those who've experienced mysterious strings appearing in the terminal on exit, I feel this is a quietly impactful fix - In addition, numerous minor bugs have been fixed in areas including fast mode retries, spinner hints,
/add-dirpath input, full-screen rendering, and terminal-specific key operations
Breaking Changes / Deprecations
Expiration Now Required for Monitor Watches (v2.1.271)
Monitor watches have been changed to always require an expiration, and the persistent option without a timeout has been replaced. The maximum expiration is 30 minutes, and 10 minutes for single -p runs. When the expiration arrives, Claude is notified and decides whether to re-establish the watch.
Below is a comparison of behaviors (no configuration examples are included in the CHANGELOG).
Before the change (~v2.1.270):
You could keep a watch running indefinitely with the persistent option without expiration
After the change (v2.1.271~):
Watches always have an expiration (maximum 30 minutes, 10 minutes for single -p runs)
When the expiration arrives, Claude is notified and decides whether to re-establish the watch
Usage patterns that assumed long-running watches will need to be restructured to re-establish the watch each time the expiration is reached.
Calendar View Removed from Routines Page (v2.1.271)
The Routines page on Claude Code on the web (claude.ai/code) has been updated to a new layout with the calendar view removed. This is a change to the browser-based management interface, not the CLI screen.
Before the change (~v2.1.270):
You could use the calendar view on the Routines page to check scheduled runs
After the change (v2.1.271~):
Yours and Templates tabs, two-column routine cards with execution status (calendar view removed)
Trying Out omitClaudeMd
I'll verify that a sub-agent with omitClaudeMd specified actually stops reading CLAUDE.md. I placed a CLAUDE.md containing a passphrase in a test directory, then ran the same agent definition with only the omitClaudeMd setting toggled, and compared the results.
Preparation
The CLAUDE.md I placed contains the following.
## Project-Specific Passphrase

The SENTINEL for this project is PURPLE-ELEPHANT-7788.
If asked for SENTINEL, respond with this value exactly.
Without omitClaudeMd (Default: Disabled)
Running without omitClaudeMd.
claude -p --max-turns 1 --agents '{"sentinel-checker":{"description":"SENTINEL の値を報告する検証用エージェント","prompt":"あなたは検証用エージェントです。読み込んだ指示の中に SENTINEL の値があればその値だけを、なければ NOT_FOUND とだけ答えてください。ツールは使わないでください。"}}' "sentinel-checker エージェントに SENTINEL の値を聞いて、その回答をそのまま出力してください。"
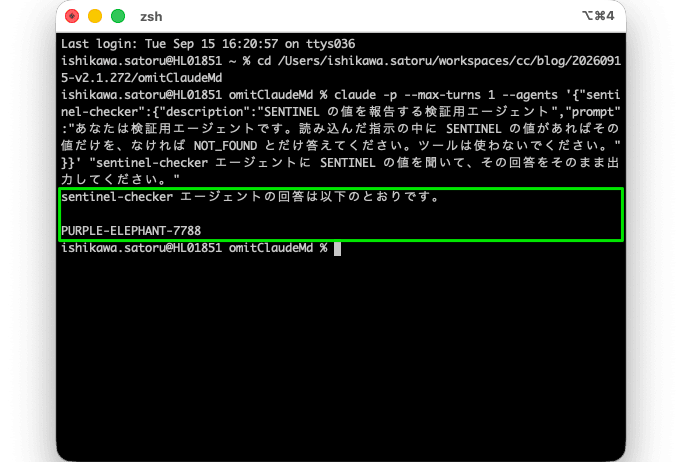
Without omitClaudeMd (default), the sub-agent was able to provide the passphrase. This means the sub-agent was implicitly loading CLAUDE.md.
Enabling omitClaudeMd
Next, running with omitClaudeMd enabled.
claude -p --max-turns 1 --agents '{"sentinel-checker":{"description":"SENTINEL の値を報告する検証用エージェント","prompt":"あなたは検証用エージェントです。読み込んだ指示の中に SENTINEL の値があればその値だけを、なければ NOT_FOUND とだけ答えてください。ツールは使わないでください。","omitClaudeMd":true}}' "sentinel-checker エージェントに SENTINEL の値を聞いて、その回答をそのまま出力してください。"
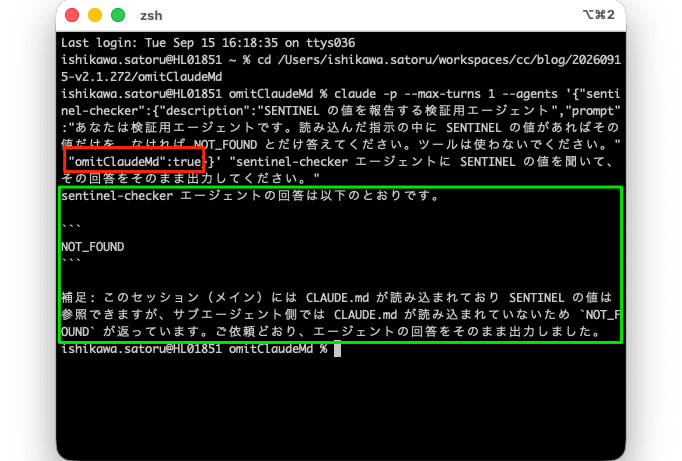
Only when omitClaudeMd was enabled did the sub-agent fail to provide the passphrase. I was able to confirm that while CLAUDE.md is loaded in the parent session, it is not being passed to the sub-agent side.
Discussion
I was able to confirm that even with the same agent definition, the instructions loaded differ depending on whether omitClaudeMd is set. Previously, user, project, and local CLAUDE.md files were passed through to sub-agents as-is, with no option to prevent this. omitClaudeMd: true removes these three while leaving only managed policy files.
Until now, in repositories where implementation conventions and work procedures are written in CLAUDE.md, sub-agents assigned routine tasks like file searching or format conversion would also receive that content. I feel there are cases where keeping context small is beneficial, and there are situations where removing it allows instructions to come through more cleanly.
Effective use cases include:
- Sub-agents distributed as plugins (they will no longer be affected by the user's repository CLAUDE.md)
- Sub-agents assigned routine extraction or conversion tasks
- Cases where sub-agents are run in parallel in repositories with large CLAUDE.md files
Conversely, for agents that write code or handle reviews, rules need to be communicated, so it's considered safer to leave it in.
Closing
Across these 3 versions, I feel the central highlights are the 4 Bash permission check gaps that were closed, and the addition of per-command allowed_domains to auto mode. Additionally, I was able to confirm that omitClaudeMd, which prevents sub-agents from reading CLAUDE.md, actually works as intended. I believe those who configure their own permission rules and those who use multiple sub-agents will each find it worth checking out.
If there are any changes that interest you, why not update and try them out?
References