Trying Out "Deletion Protection," a New Feature of Amazon CloudWatch Logs

This page has been translated by machine translation. View original
On November 26, 2025, Amazon CloudWatch Logs added support for a new feature: "Deletion Protection."
Until now, deletion protection has been available for S3 buckets, RDS instances, ALBs, and so on, but CloudWatch Logs had no equivalent feature. As a result, the means of protecting important logs were limited to things like IAM policies (Deny Action), but with this update, you can explicitly configure protection on a per-log-group basis.
In this article, I introduce the results of testing this new feature using the AWS CLI.
Feature Overview
For a log group with deletion protection enabled, delete operations (DeleteLogGroup) are rejected. This prevents the risk of audit logs and important application logs being lost due to operational mistakes or script malfunctions.
- Scope: Per log group
- Default: Disabled (both for existing log groups and when creating new ones)
- Release: Cannot be deleted unless protection is explicitly disabled
Web Console
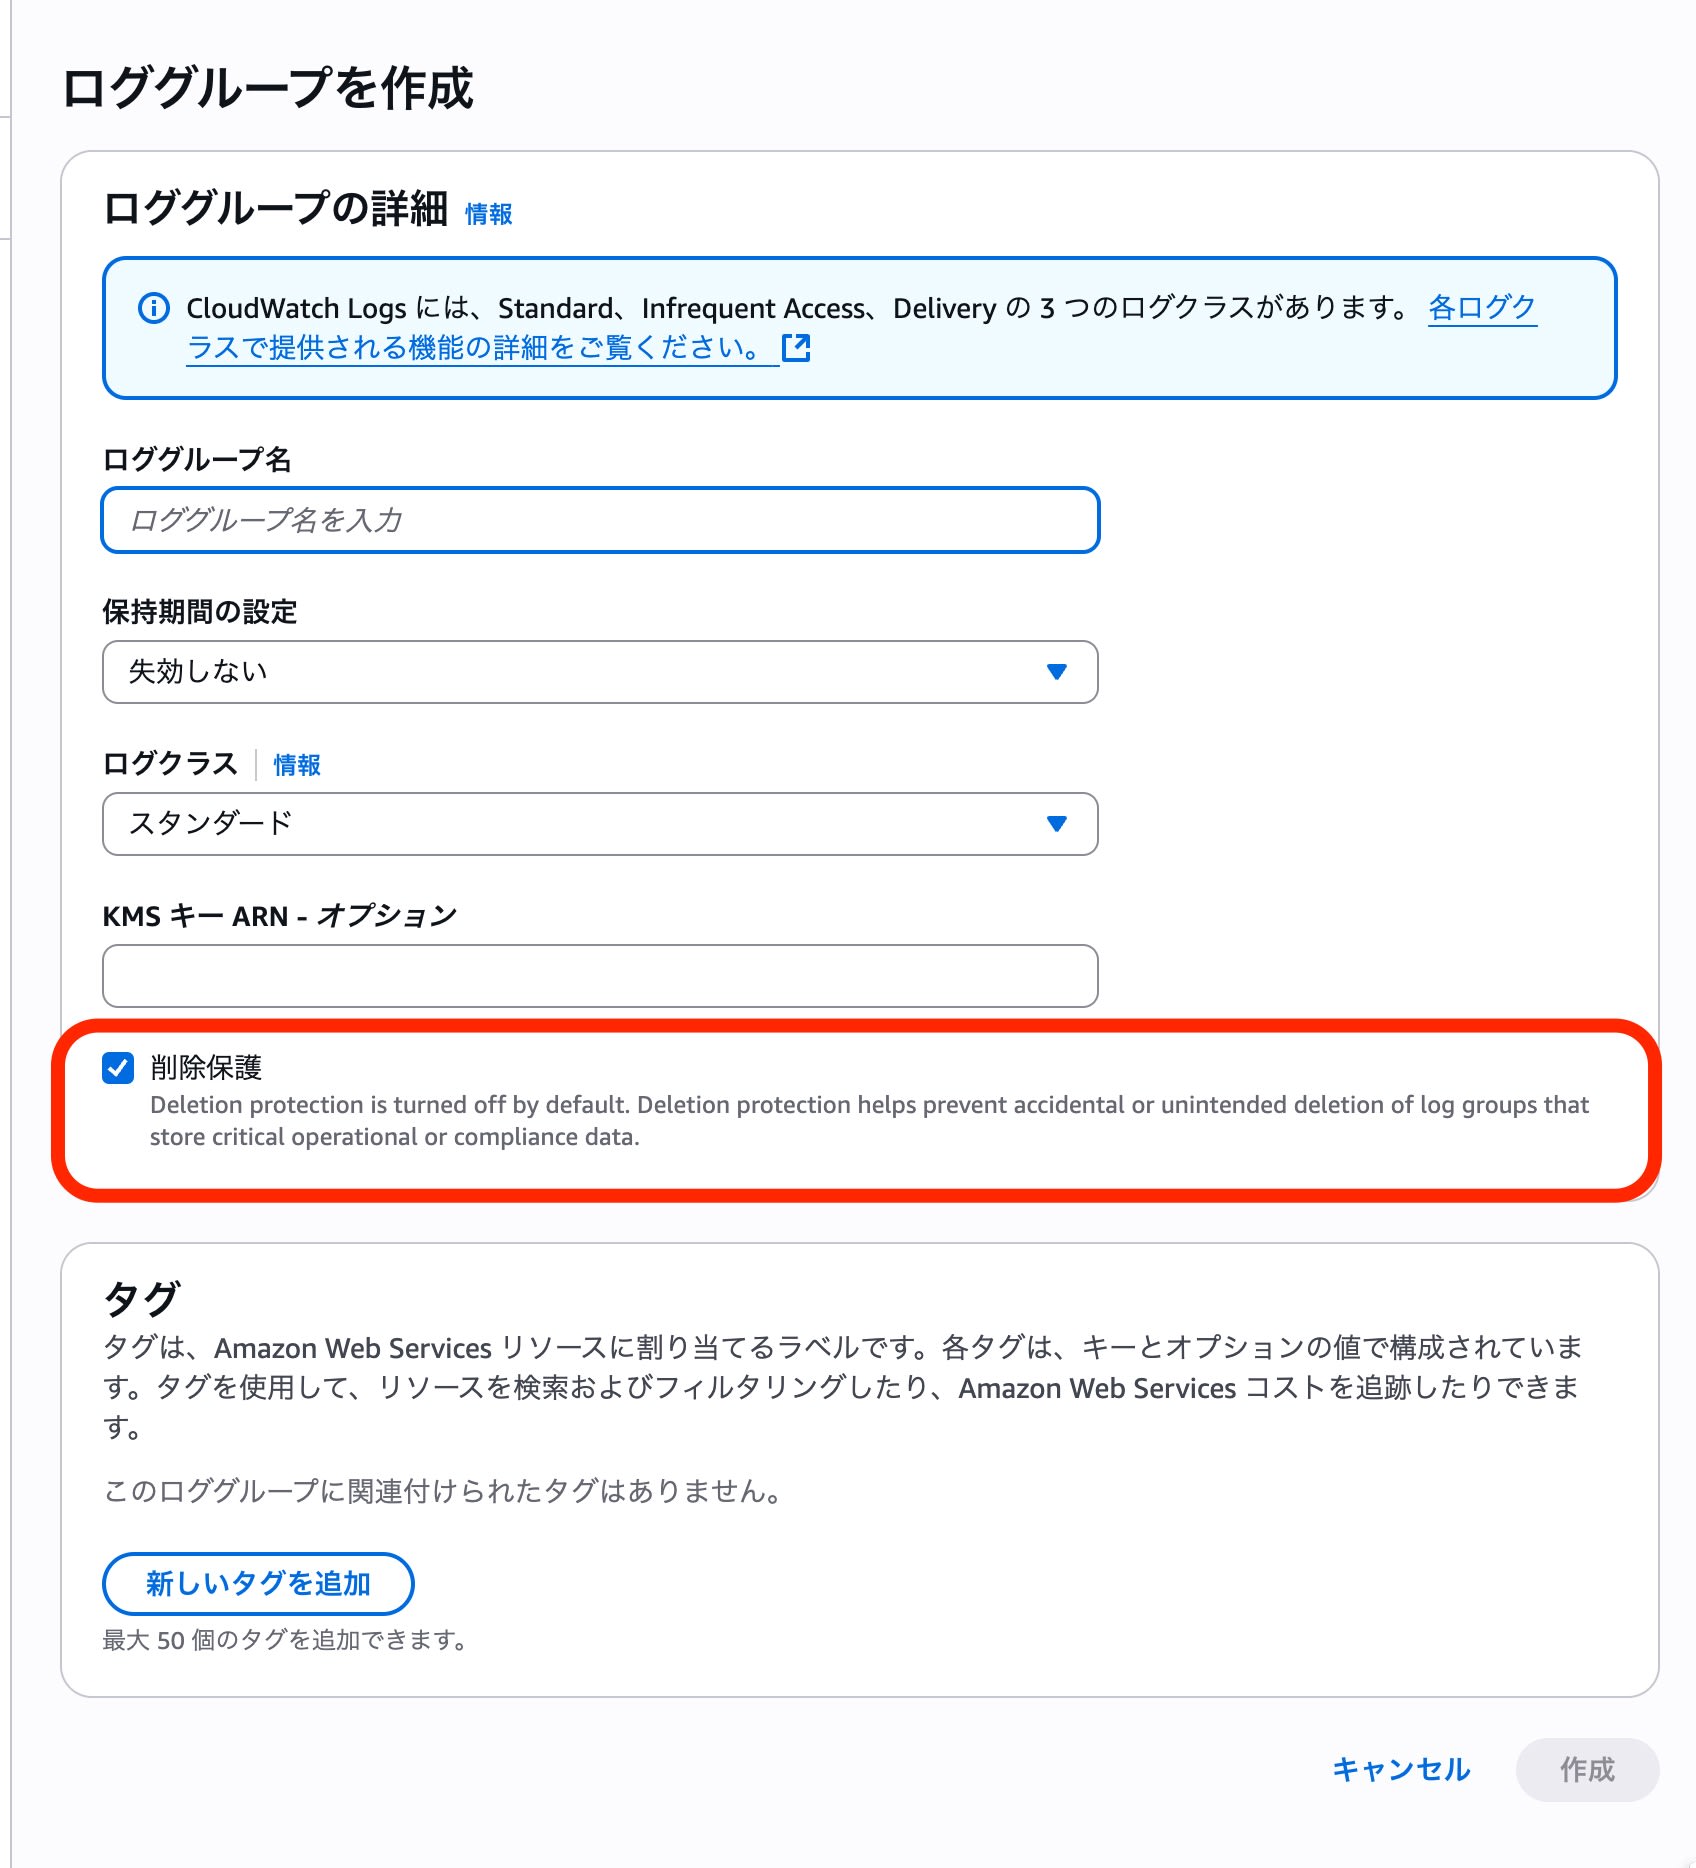
When I checked the management console, a "Deletion protection" checkbox had been added to the log group creation screen. You can configure it simply by enabling it here.
Test Environment
I used the following environment in the Tokyo region for testing. The AWS CLI has been updated to the latest version that supports this feature.
OS: Amazon Linux 2023
Kernel: 6.1.158-178.288.amzn2023.x86_64
AWS CLI: 2.32.6
Python: 3.13.9
$ aws --version
aws-cli/2.32.6 Python/3.13.9 Linux/6.1.158-178.288.amzn2023.x86_64 exe/x86_64.amzn.2023 prompt/off
Test 1: Enabling Deletion Protection and Checking Behavior
1. Creating a Log Group and Configuring Protection
Create a log group for testing and enable deletion protection from the CLI.
# ロググループ作成
aws logs create-log-group --log-group-name /test/protection-demo

# 削除保護を有効化
aws logs update-log-group \
  --log-group-name /test/protection-demo \
  --deletion-protection-enabled
Check the status after configuration. I confirmed that a deletionProtectionEnabled field has been added to the output of describe-log-groups.
aws logs describe-log-groups \
  --log-group-name-prefix /test/protection-demo \
  --query 'logGroups[].{Name:logGroupName, Protected:deletionProtectionEnabled}'
Execution result:
[
    {
        "Name": "/test/protection-demo",
        "Protected": true
    }
]
The log shows Protected: true, so I concluded that the setting was applied.
2. Attempting Deletion (With Protection)
In this state, I tried to delete the log group.
aws logs delete-log-group --log-group-name /test/protection-demo
Execution result (error log):
An error occurred (InvalidParameterException) when calling the DeleteLogGroup operation: The log group '/test/protection-demo' cannot be deleted because deletion protection is enabled.
As expected, an InvalidParameterException occurred, and I confirmed that deletion was blocked.
3. Releasing Protection and Deleting
Disable deletion protection, then try deleting again.
# 保護を解除
aws logs update-log-group \
  --log-group-name /test/protection-demo \
  --no-deletion-protection-enabled

# 削除実行
aws logs delete-log-group --log-group-name /test/protection-demo
No error was output, and the command finished normally. When I ran describe-log-groups again, I confirmed that the resource no longer existed (an empty list was returned).
Test 2: CloudFormation Support Status
Assuming use in environments managed with IaC, I investigated the support status in CloudFormation (CFn).
Test Template
I created the following YAML and tried deploying it. I guessed the property name to be DeletionProtectionEnabled based on the conventions of other AWS resources (such as RDS).
AWSTemplateFormatVersion: '2010-09-09'
Resources:
  ProtectedLogGroup:
    Type: AWS::Logs::LogGroup
    Properties:
      LogGroupName: /test/cfn-protection
      RetentionInDays: 7
      DeletionProtectionEnabled: true  # 検証箇所
Result: Deployment Failed
When I ran the deployment, the following error occurred.
Resource handler returned message: "Model validation failed (#/DeletionProtectionEnabled: #: only 1 subschema matches does not match the schema)"
I also checked the CloudFormation resource schema with the AWS CLI.
aws cloudformation describe-type \
  --type RESOURCE \
  --type-name AWS::Logs::LogGroup \
  --query 'Schema' \
  --output text
The property DeletionProtectionEnabled did not exist in the output JSON schema.
Conclusion:
As of this writing, CloudFormation does not natively support this property. To apply deletion protection to log groups managed by CFn, one of the following approaches is required.
- Call the API using a Custom Resource (Lambda).
- Configure it separately via the AWS CLI / Management Console after provisioning
Application to Operations (Bulk Update)
I checked whether the setting can also be applied to existing log groups.
Below is an example script that applies deletion protection in bulk to all log groups with a specific prefix (e.g., /aws/lambda/).
LOG_PREFIX="/aws/lambda/"

aws logs describe-log-groups --log-group-name-prefix "${LOG_PREFIX}" \
  --query 'logGroups[].logGroupName' --output text | \
while read -r log_group; do
  echo "Enabling deletion protection for: ${log_group}"
  aws logs update-log-group \
    --log-group-name "${log_group}" \
    --deletion-protection-enabled
done
After running it, I confirmed that the target log groups showed deletionProtectionEnabled: true.
Summary
I tested the deletion protection feature of Amazon CloudWatch Logs.
- CLI: I confirmed that it can easily be enabled and disabled with
update-log-group(or related APIs). - Behavior: When protection is enabled, the
DeleteLogGroupAPI clearly returns an error, preventing accidental deletion. - IaC: CloudFormation does not support it as of this writing, so supplementing with the CLI or similar is necessary.
Please make use of it for systems with strict compliance requirements, where audit logs that need long-term retention must be kept in CloudWatch Logs.
As for CloudFormation, which was not supported at the time of writing, I expect there will be challenges such as how it is handled when a stack is deleted, but I look forward to its support.
