Setting Up Email Authentication (DKIM / SPF / DMARC) with Amazon SES and Understanding How It Works

This page has been translated by machine translation. View original
I think many of you remember that in 2024, Gmail made email authentication of the sending domain mandatory in its "Email sender guidelines". Today, email authentication (DKIM / SPF / DMARC) is effectively required for businesses to send email. I recently had the opportunity to set up Amazon SES from scratch, so I'd like to understand how it all works while setting it up, including email authentication.
Registering a Domain
First, register the sender domain of the emails you will send from SES. In this step, SES verifies the user's ownership of the domain. Once verified, the user can send emails with From addresses on that domain.
Setup
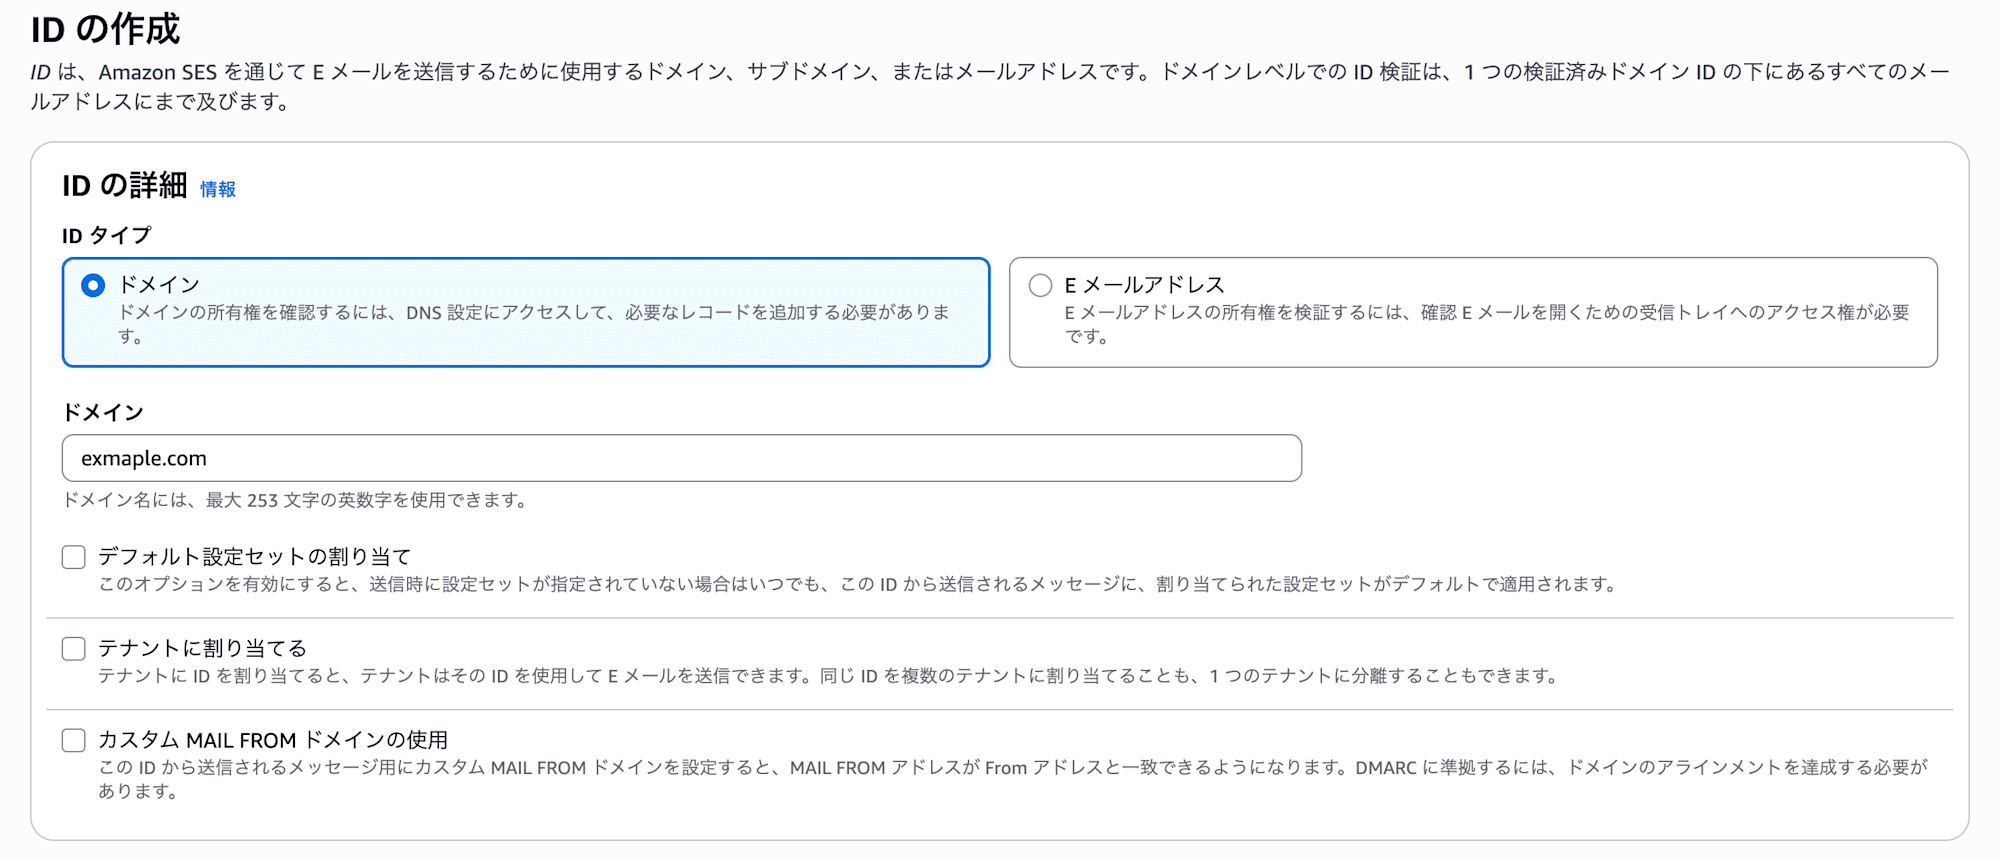
In the SES console, go to Identities > Create identity, select Identity type: Domain, and enter the domain name.
Under Advanced DKIM settings > Identity type, select "Easy DKIM".
This time I used an external DNS rather than Route53, so I unchecked the option to publish to Route53 and registered the DNS records manually.
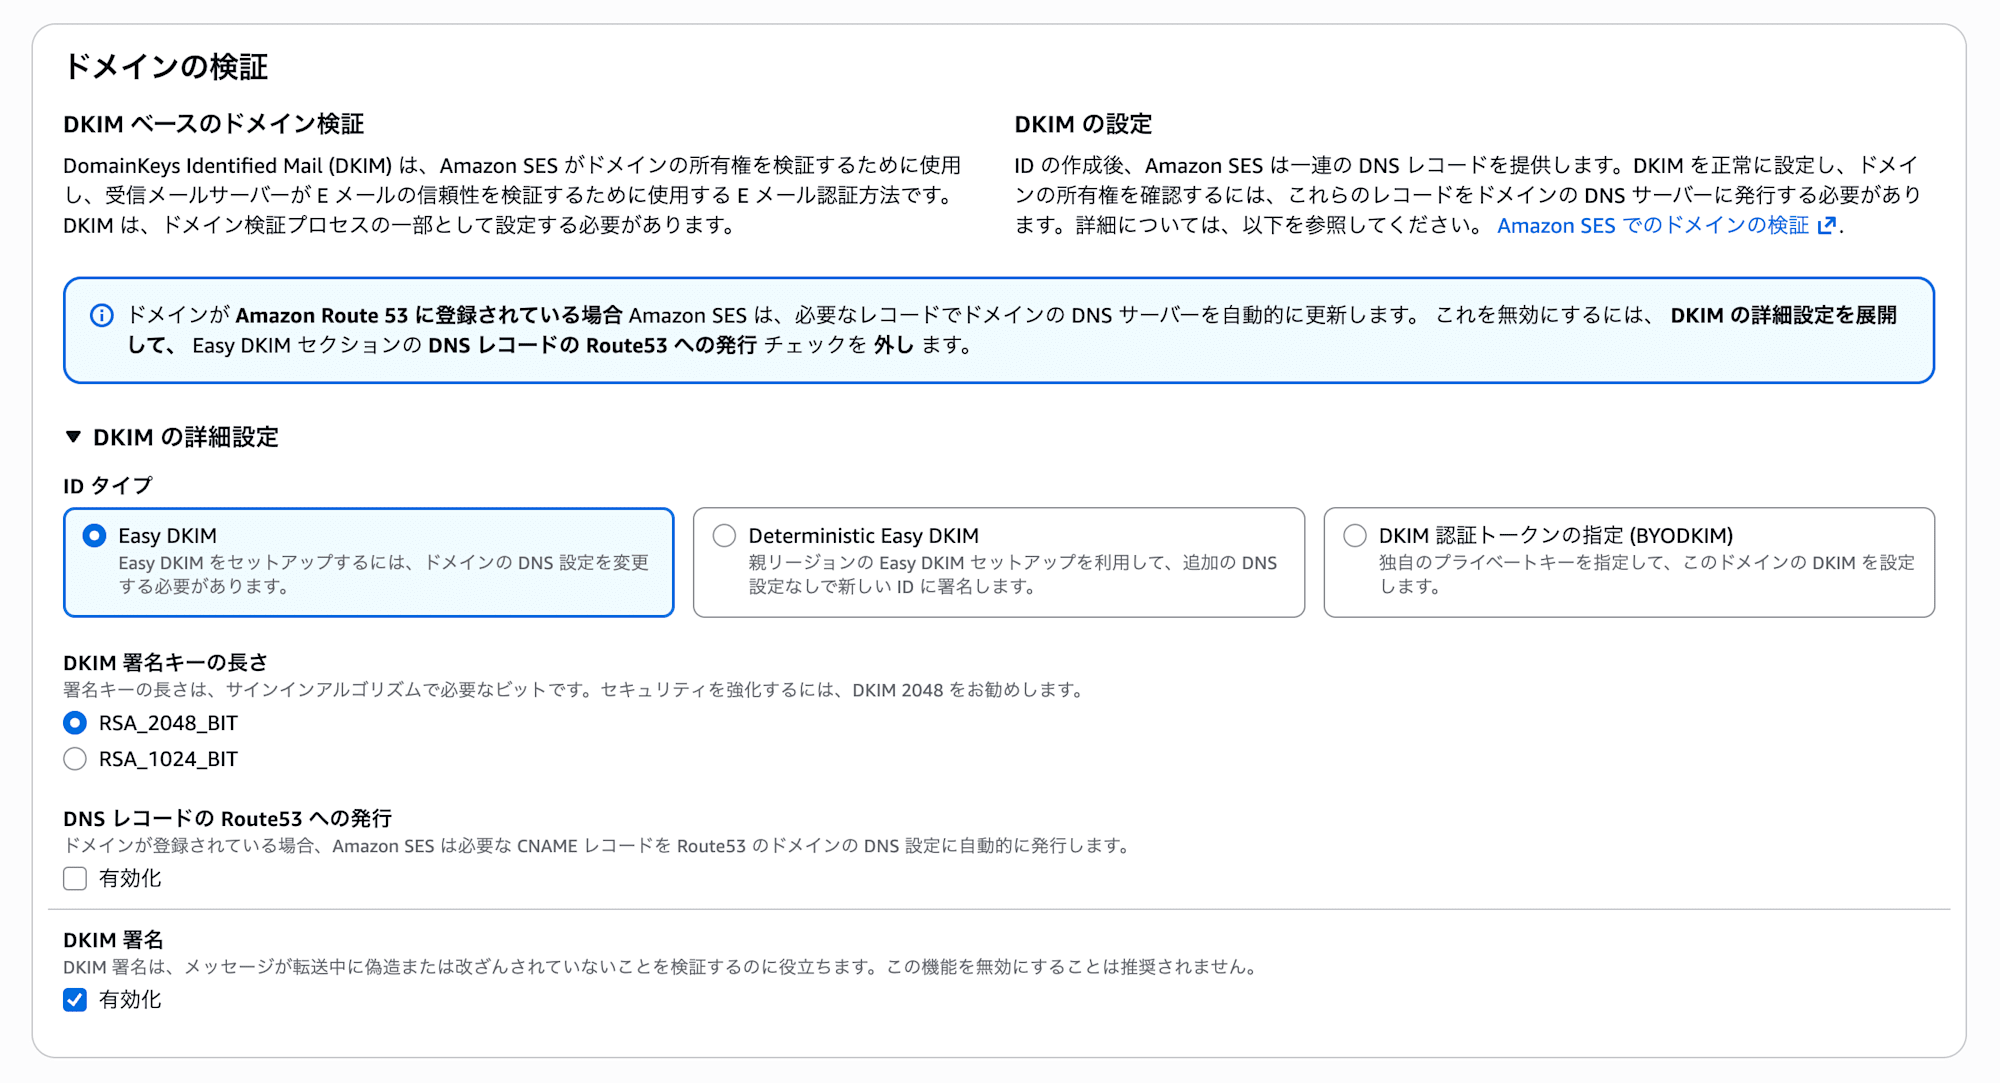
"Easy DKIM" is a service that manages and distributes the keys used for DKIM signing, which I'll describe later.
SES confirms domain verification (ownership) by checking that the DKIM DNS records are registered, so let's continue on to the DKIM setup.
DKIM (DomainKeys Identified Mail)
DKIM is a mechanism that attaches a signature to outgoing emails to verify that the email has not been tampered with.
Setup
This time I'll use "Easy DKIM", which automatically manages the private key and distributes the public key required for DKIM. (Alternatively, you can manage the keys yourself.)
When you select Easy DKIM, DNS records are generated so that the public key distributed by Easy DKIM can be looked up via DNS. Register these in the DNS of the sender domain.
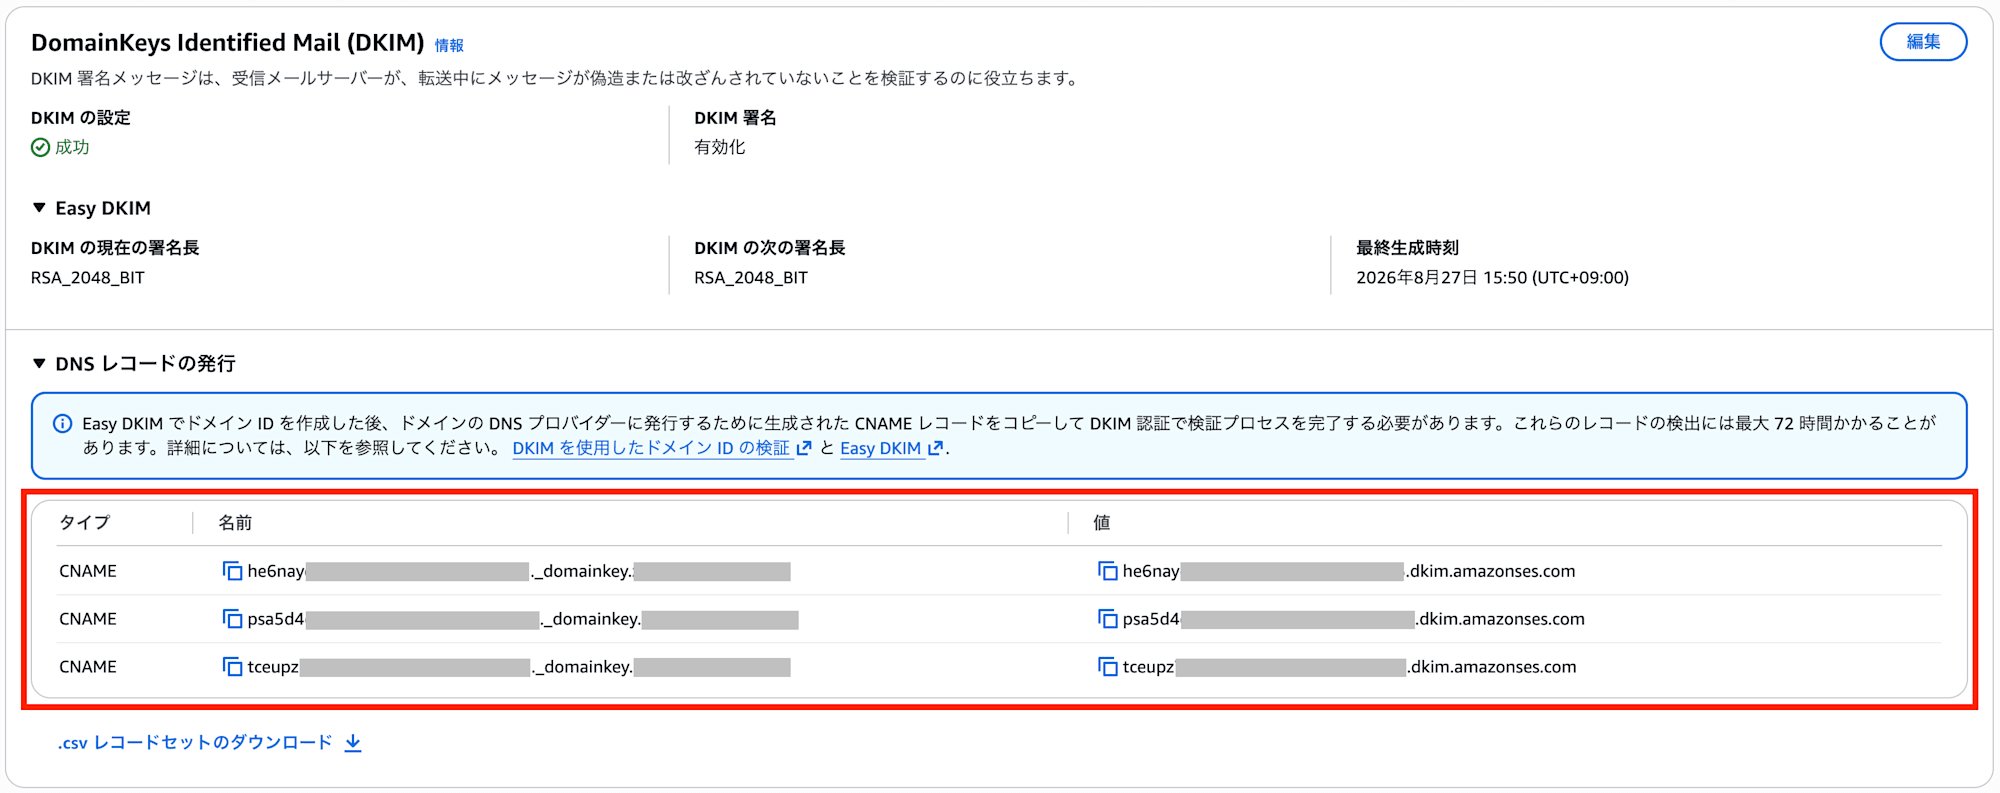
The record format is CNAME <token>._domainkey.<sending domain> <token>.dkim.amazonses.com.
※ token is the key identifier.
How Verification Works
The DKIM signature is added as follows.
- Hash the main headers of the email (From / Subject / Date / To, etc.) and the body separately
- Sign those hashes with the private key
- Attach the result to the email as the
DKIM-Signatureheader
Here is what an actual header looks like (you can see it with "Show original" in Gmail).
DKIM-Signature: v=1;
                a=rsa-sha256;
                d=<送信ドメイン>;
                s=<token>;
                h=From:To:Subject:Date:...;
                bh=<ハッシュ>;
                b=<署名>
The receiving mail server looks up the public key using the information in the DKIM-Signature header.
- From
d=<sending domain>ands=<token>, construct the<token>._domainkey.<sending domain>registered in the CNAME record. - Get
<token>.dkim.amazonses.comfrom the CNAME. - Get the TXT record of
<token>.dkim.amazonses.comto obtain the public key.
Finally, the signature is verified with the public key. If the results match, it is "DKIM=PASS".
SPF (Sender Policy Framework)
SPF verifies that the IP of the sending mail server matches the IP addresses registered in the DNS of the MAIL FROM domain (also called the envelope From; note that this is not the domain of the From address).
By default in SES, amazonses.com is set as this envelope From. This alone satisfies the SPF requirements, but it does not satisfy part of the DMARC requirements (that the envelope From matches the domain of the From address). The DMARC pass criterion is satisfying at least one of DKIM or SPF, so leaving it as is would be fine, but by configuring a "custom MAIL FROM domain" you can make the envelope From a custom domain. The steps are shown below.
Setting Up a Custom MAIL FROM Domain
On the page of the registered domain, configure the custom MAIL FROM domain. Because the envelope From must be an address that can receive bounces, the bounce.<sender domain> subdomain is conventionally used. After registration, two records to register in DNS are issued: an MX record for receiving bounces in SES (to satisfy the requirement above), and a TXT record required for SPF verification.
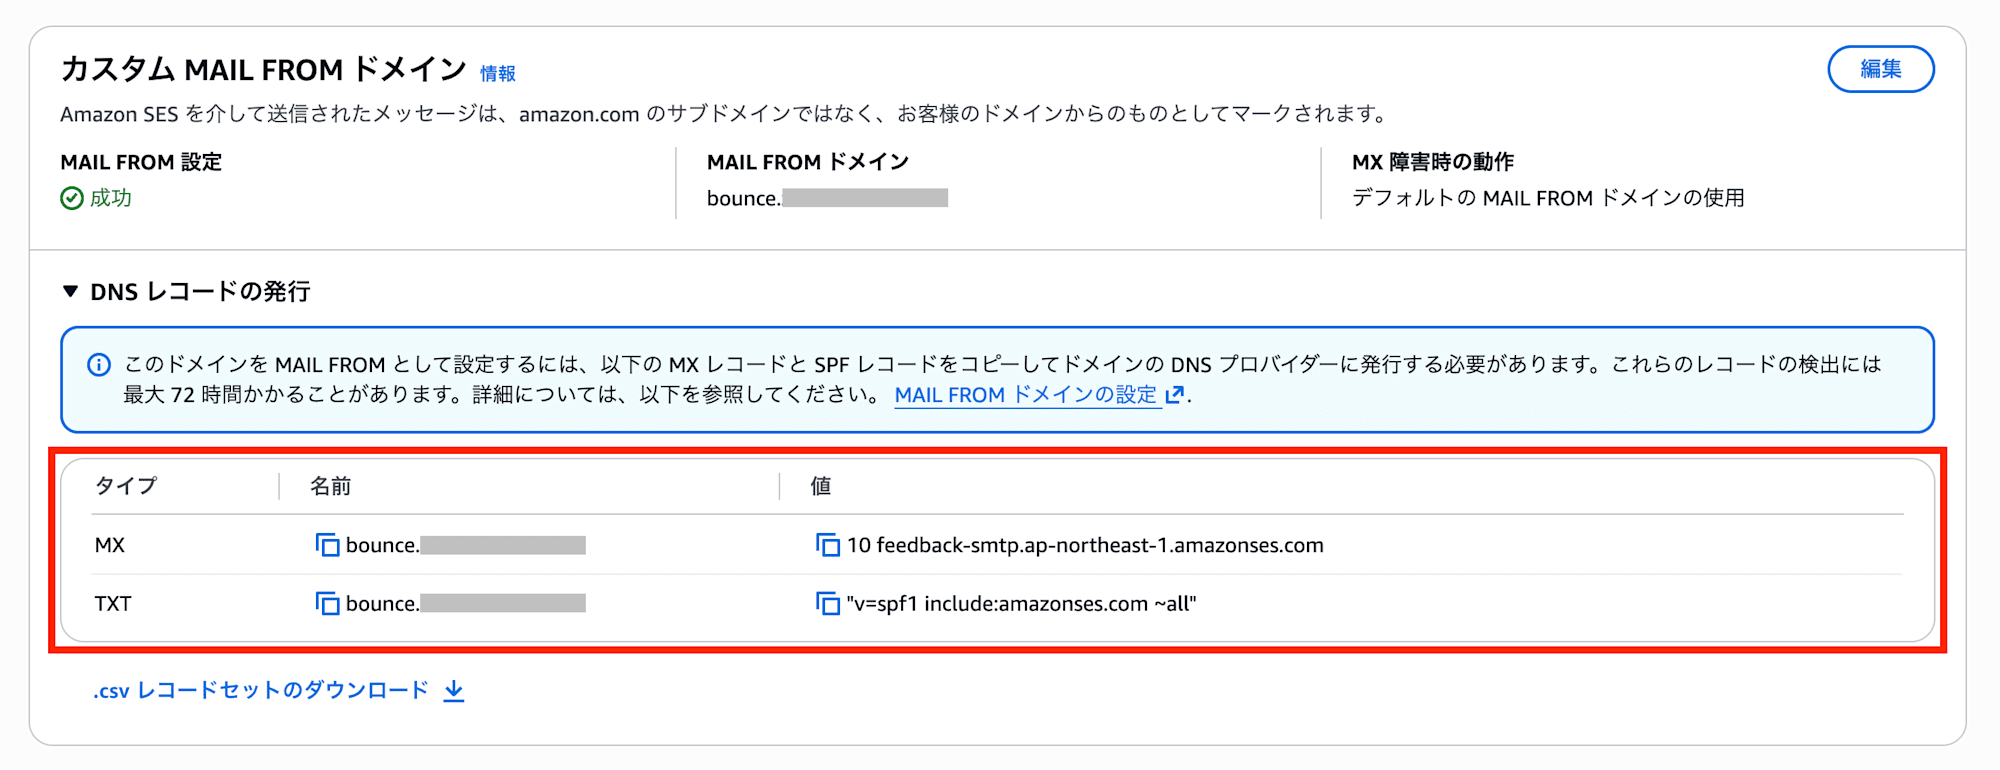
Once these are registered, the setup is complete, and the envelope From (specifically, the value of the Return-Path header, etc.) becomes that of the registered domain.
Before:
<一意なID>@<リージョン>.amazonses.com
After:
<一意なID>@bounce.<送信元ドメイン>
How Verification Works
-
Look up the TXT record for the domain in the envelope From
dig bounce.<sender domain> TXT
→ "v=spf1 include:amazonses.com ~all" -
Look up the TXT record for the included domain as well
dig amazonses.com TXT
→ "v=spf1 ip4:199.255.192.0/22 ip4:54.240.0.0/18 … -all"
The ip4: entries in this are checked in order to verify whether the sender's IP address is included in the list.
DMARC (Domain-based Message Authentication, Reporting, and Conformance)
DKIM verified that "the email is from the signing domain and has not been tampered with", and SPF verified that "the domain and IP of the mail server are correct". However, there remains the possibility that an attacker has configured these two correctly and only the From email address is spoofed. DMARC closes this gap by performing verification of the From address.
Setup
SES is not involved in DMARC. Register the following record on your DNS server.
TXT _dmarc.<Fromのドメイン> <内容>
The contents of the TXT record are as follows.
| Key | Value |
|---|---|
| v= | DMARC1 (fixed) |
| p= | Action on failure. reject: reject the email, quarantine: send to spam, none: do nothing |
| rua= | Destination for aggregate reports. The receiving server sends XML once a day saying "how many emails came from which IP and what the SPF/DKIM results were". |
| ruf= | Destination for failure reports. Sends details (headers, etc.) for each failed email. |
| fo= | Condition for sending failure reports. 1: send if either SPF or DKIM fails (the default 0 sends only when both fail) |
As you can see, a destination for the reports is required. In my project, I use a service called EASYDMARC.
How Verification Works
- Verify that the DKIM result is PASS and that the verified domain matches the domain of the From address
- Verify that the SPF result is PASS and that the verified domain matches the domain of the From address
- If either 1 or 2 is OK, DMARC is PASS. If it fails, the email is handled according to the DMARC policy (the one registered during setup)
The End
I was able to deepen my understanding of email authentication by researching it myself. I hope this helps your understanding as well.
