I Tried Connecting Claude Code to Claude Platform on AWS Using IAM Authentication (SigV4)

This page has been translated by machine translation. View original
Claude Platform on AWS became GA today. The setup and API call verification are summarized in the previous article.
Continuing from that, this time I verified how to run Claude Code via Claude Platform on AWS. You can consolidate usage fees into your AWS bill, and with SigV4 authentication you can also manage permissions based on IAM.
For the differences from Bedrock, see here:
What This Article Covers / Doesn't Cover
Recommended for people who:
- Want to consolidate Claude Code usage fees into their AWS bill
- Want to use Claude's latest models and native latest features right away
- Want to govern permissions for development tools with IAM
This article verifies the following.
- Environment variable settings to point Claude Code at Claude Platform on AWS
- Verifying operation with SigV4 authentication (AWS IAM Identity Center)
- Verifying operation with API key authentication
- Checking settings with the
/statuscommand - Running an actual coding task
- Operation with EC2 + IAM role
- Verifying that usage is reflected on the Claude Console Usage page
Not covered:
- Initial setup of Claude Platform on AWS (see the previous article)
- Detailed design of IAM policies
- Configurations via an LLM gateway
- Cowork (Claude Desktop) integration (to be verified in a separate article)
Prerequisites:
- Claude Platform on AWS is already set up (you have completed everything up to Workspace creation in the previous article)
- You have obtained your Workspace ID (check under Claude Platform on AWS → Workspaces in the AWS console)
- Claude Code is installed
- AWS CLI v2 + IAM Identity Center are configured (when trying SigV4 authentication)
- The IAM role used for SigV4 authentication has been granted permissions to call Claude Platform on AWS
Verification Environment
| Item | Value |
|---|---|
| OS | macOS / Linux (Ubuntu) |
| Claude Code | 2.1.139 |
| AWS CLI | aws-cli/2.34.39 |
| Workspace region | ap-northeast-1 |
| Authentication method | AWS IAM Identity Center / API key / IAM role |
| Verification environment 2 (advanced) | EC2 (Amazon Linux 2023, t3.small) |
Configuration Overview
Three environment variables are required.
export CLAUDE_CODE_USE_ANTHROPIC_AWS=1
export ANTHROPIC_AWS_WORKSPACE_ID=wrkspc_xxxxxxxxxxxxx
export AWS_REGION=ap-northeast-1
Environment variable list:
| Environment variable | Required | Description |
|---|---|---|
CLAUDE_CODE_USE_ANTHROPIC_AWS |
✅ | Enabled with 1 |
ANTHROPIC_AWS_WORKSPACE_ID |
✅ | Workspace ID (wrkspc_ format) |
AWS_REGION |
✅ | Match the region where you created the Workspace |
ANTHROPIC_AWS_API_KEY |
△ | For API key authentication. When set, it takes precedence over SigV4 |
ANTHROPIC_AWS_BASE_URL |
— | Only when using an LLM gateway |
Connecting with SigV4 Authentication (AWS IAM Identity Center)
# 1. AWS IAM Identity Center でログイン
aws sso login --profile my-profile
export AWS_PROFILE=my-profile

# 2. 認証状態を確認
aws sts get-caller-identity
{
    "UserId": "AROAXXXXXXXXXXXXXXXXX:example-user",
    "Account": "123456789012",
    "Arn": "arn:aws:sts::123456789012:assumed-role/example-sso-role/example-user"
}
# 3. Claude Platform on AWS を有効化
export CLAUDE_CODE_USE_ANTHROPIC_AWS=1
export ANTHROPIC_AWS_WORKSPACE_ID=wrkspc_xxxxxxxxxxxxx
export AWS_REGION=ap-northeast-1

# 4. 競合する設定を解除
unset CLAUDE_CODE_USE_BEDROCK
unset CLAUDE_CODE_USE_FOUNDRY
unset ANTHROPIC_AWS_API_KEY

# 5. Claude Code 起動
claude
At the time of verification, "Opus 4.7 · API Usage Billing" was displayed at startup.
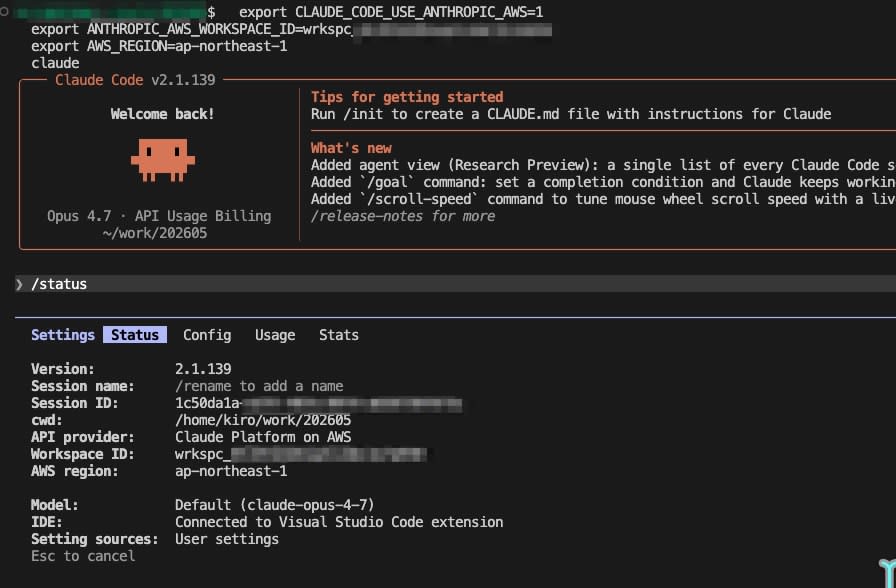
Check the following with /status.
| Item | Value |
|---|---|
| API provider | Claude Platform on AWS |
| Workspace ID | wrkspc_xxxxxxxxxxxxx |
| AWS region | ap-northeast-1 |
| Model | Default (claude-opus-4-7) |
Connecting with API Key Authentication (for Environments Where SigV4 Is Unavailable)
export CLAUDE_CODE_USE_ANTHROPIC_AWS=1
export ANTHROPIC_AWS_WORKSPACE_ID=wrkspc_xxxxxxxxxxxxx
export AWS_REGION=ap-northeast-1
export ANTHROPIC_AWS_API_KEY="YOUR_CLAUDE_PLATFORM_ON_AWS_API_KEY"

claude
- Setting
ANTHROPIC_AWS_API_KEYtakes precedence over SigV4 - Use an API key generated on the Claude Platform on AWS → "API keys" page in the AWS console. It is separate from a regular Anthropic API key (issued for a personal account or a different Organization)
Verification with a Real Task
With SigV4 authentication configured, I ran an actual coding task.
> PythonでFizzBuzzを書いて。1から30まで出力するスクリプトを作成して
Everything worked as usual, from Claude Code creating the file to running Python and checking the output.
for i in range(1, 31):
    if i % 15 == 0:
        print("FizzBuzz")
    elif i % 3 == 0:
        print("Fizz")
    elif i % 5 == 0:
        print("Buzz")
    else:
        print(i)
Execution result:
1
2
Fizz
4
Buzz
...
14
FizzBuzz
16
...
29
FizzBuzz
I confirmed that usage was reflected on the Claude Console Usage page (AWS console → Claude Platform on AWS → Access → Sign in → Usage).
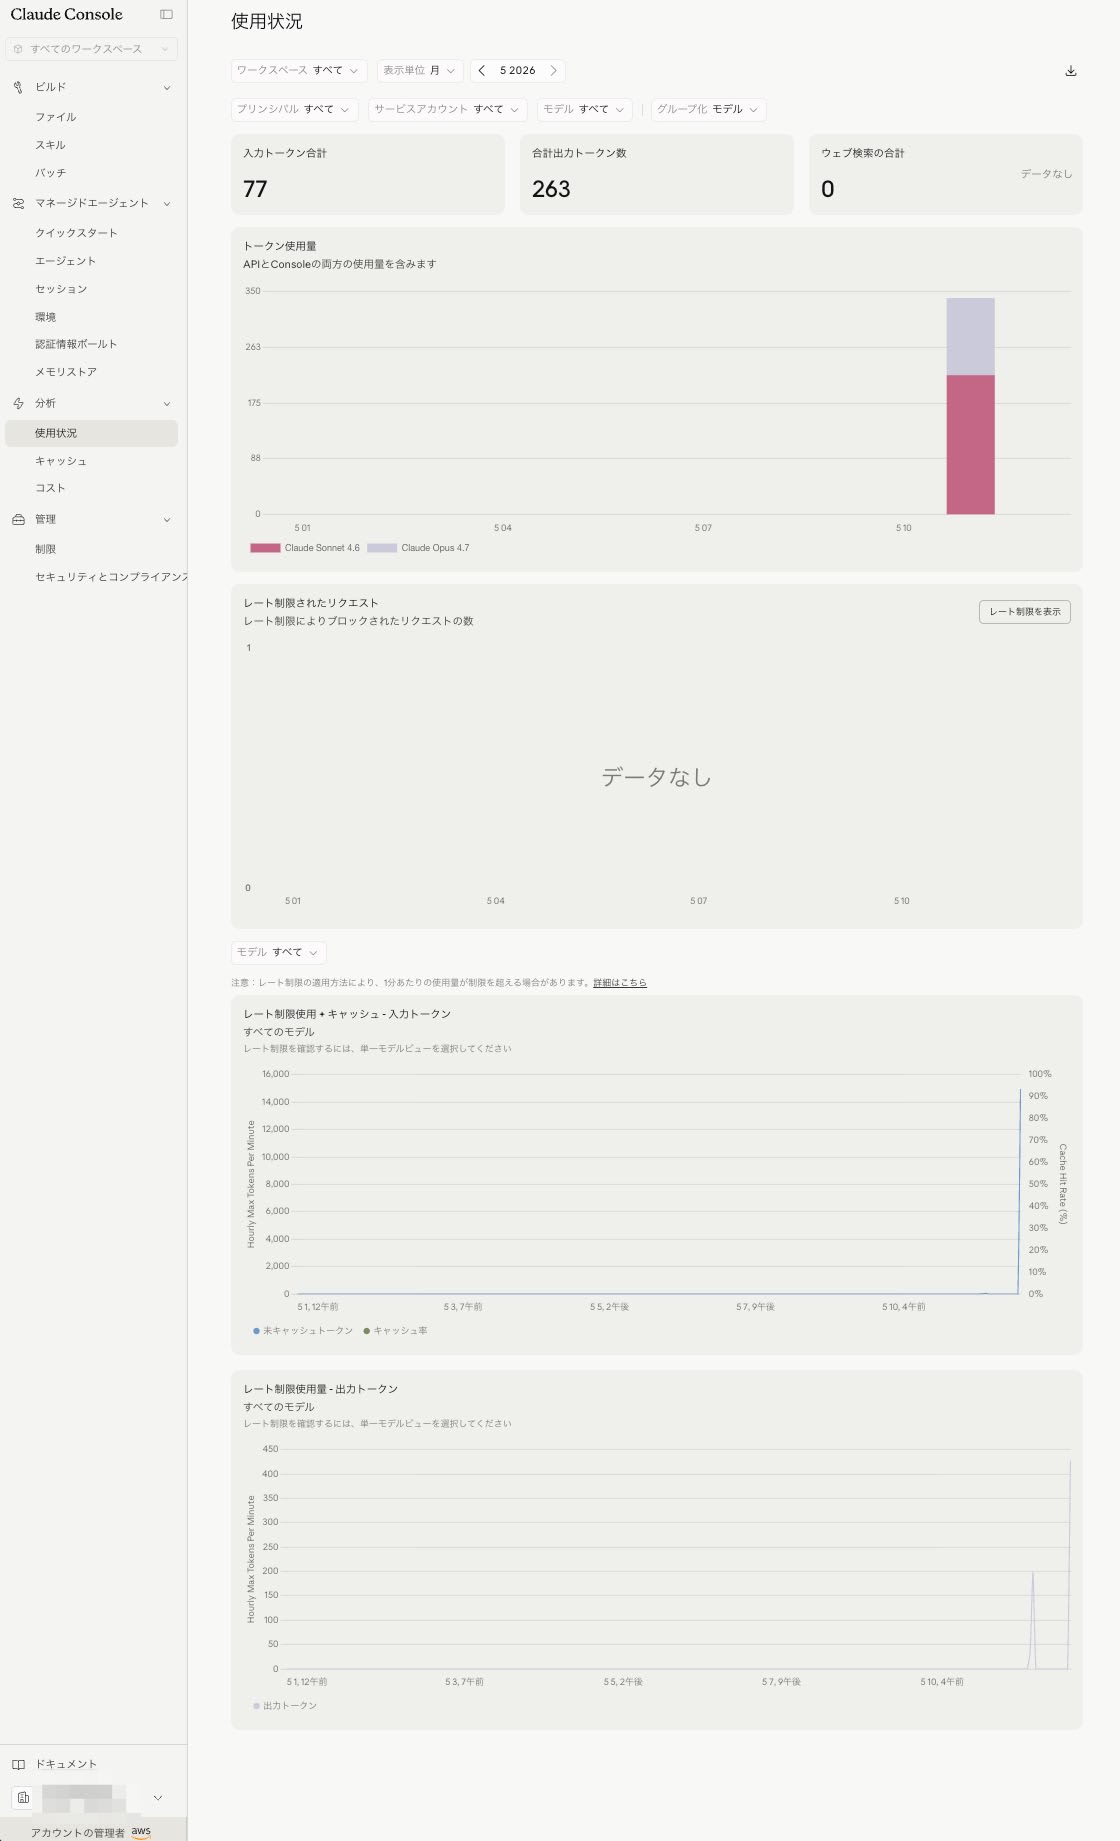
Input tokens and output tokens are displayed per model. In this verification, in addition to Opus 4.7, I could also see Haiku 4.5 usage accompanying the use of Claude Code. Depending on model settings and what is executed, usage for multiple models may be recorded.
【Advanced】Keyless Operation with EC2 + IAM Role (for CI/CD)
AWS IAM Identity Center assumes interactive login by a human. Here, we confirm that Claude Code works with only an EC2 instance profile (IAM role).
Verification setup:
- EC2 instance (Amazon Linux 2023 / t3.small)
- A verification IAM role attached to the instance profile
- No interactive login / access keys / API keys at all
IAM Policy
Operation was confirmed with the following policy.
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Effect": "Allow",
      "Action": [
        "aws-external-anthropic:CreateInference"
      ],
      "Resource": "arn:aws:aws-external-anthropic:ap-northeast-1:123456789012:workspace/wrkspc_xxxxxxxxxxxxx"
    },
    {
      "Effect": "Allow",
      "Action": [
        "sts:GetWebIdentityToken",
        "sts:TagGetWebIdentityToken"
      ],
      "Resource": "*"
    }
  ]
}
Steps to Run on EC2
# Claude Code インストール
curl -fsSL https://claude.ai/install.sh | bash

# 環境変数のみ設定(対話ログイン/アクセスキー/API key は一切不要)
export CLAUDE_CODE_USE_ANTHROPIC_AWS=1
export ANTHROPIC_AWS_WORKSPACE_ID=wrkspc_xxxxxxxxxxxxx
export AWS_REGION=ap-northeast-1

# 認証確認(インスタンスプロファイルのロールが返る)
aws sts get-caller-identity
{
    "UserId": "AROAXXXXXXXXXXXXXXXXX:i-0123456789abcdef0",
    "Account": "123456789012",
    "Arn": "arn:aws:sts::123456789012:assumed-role/example-ec2-role/i-0123456789abcdef0"
}
# Claude Code 起動(非対話モード)
claude -p "Say hello" --output-format json
With
-p(specify a prompt) and--output-format json, you get non-interactive execution and structured output. This form looks easy to use for CI/CD purposes. However, for tasks involving file changes or command execution, you need to separately consider Claude Code's permission settings and approval flow.
I confirmed that a response is returned with just the EC2 instance profile and only three environment variables. Since you don't need to hold access keys or API keys, you can reduce the risk of leaking long-lived secrets.
This setup looks applicable to GitHub Actions self-hosted runners (EC2), CodeBuild, EC2-based remote development environments, and more.
Advantages Compared to Going Through Bedrock
The previous article introduced things like "native experience" and "same-day availability of new features." Here, also drawing on the official documentation, I summarize the elements worth noting as differences from going through Bedrock.
| Element | Details |
|---|---|
| Separate capacity pool | Treated as a different capacity pool from Bedrock, so you can consider using it alongside Bedrock as a failover destination |
| Cache not counted in ITPM | cache_read_input_tokens is not counted toward rate limits |
| PrivateLink support | Private network connection from a VPC is possible (not verified in this article) |
We cannot assert that "rate limits are higher than Bedrock." The advantage is the "separate capacity pool," which allows a failover configuration when used together with Bedrock. Specifications may change, so check the latest official documentation before use.
Limitations and Troubleshooting
Limitations:
| Item | Details |
|---|---|
| Claude Code workspace | Not supported (the Claude Code-specific rate limit screen is unavailable) |
/login /logout |
Not relevant (authentication is by AWS credentials or API key) |
| Coexistence with Bedrock/Foundry | Explicit unset is required |
| Fixed at Tier 1 | No automatic promotion |
Troubleshooting:
| Symptom | What to check |
|---|---|
| Provider doesn't switch | Check CLAUDE_CODE_USE_ANTHROPIC_AWS=1 |
| Bedrock is used | Unset CLAUDE_CODE_USE_BEDROCK / CLAUDE_CODE_USE_FOUNDRY |
| API key takes precedence | Unset ANTHROPIC_AWS_API_KEY |
| 403 / AccessDenied | Check authentication with aws sts get-caller-identity. Check IAM permissions (including sts:GetWebIdentityToken) |
| SSO expired | Re-run aws sso login |
| Workspace not found | Check that AWS_REGION matches the Workspace's region |
Summary
| Verification item | Result |
|---|---|
| SigV4 authentication (IAM Identity Center) | ✅ |
| API key authentication | ✅ |
| Code generation, file operations, command execution | ✅ |
| EC2 + IAM role (keyless) | ✅ |
| Usage page reflection | ✅ |
With three environment variables, Claude Code worked via Claude Platform on AWS. Since we confirmed that it also works with SigV4 authentication on EC2 + an instance profile, there is room for application to CI/CD environments and remote development environments.
At least in this configuration, we confirmed that the IAM policy needs sts:GetWebIdentityToken / sts:TagGetWebIdentityToken in addition to aws-external-anthropic:CreateInference.
Cleanup after verification:
unset CLAUDE_CODE_USE_ANTHROPIC_AWS
unset ANTHROPIC_AWS_WORKSPACE_ID
unset ANTHROPIC_AWS_API_KEY
When returning to Bedrock or the direct API, unset the above. If you changed
AWS_REGIONorAWS_PROFILEfor verification, restore them as needed.
Quick comparison (see the previous article for details):
| Aspect | Claude Platform on AWS | Bedrock |
|---|---|---|
| API compatibility | Anthropic Messages API as is | Bedrock format |
| New features | Same-day release | Depends on Bedrock's schedule |
| Capacity pool | Independent (failover possible) | Bedrock's own |
| Billing | Consolidated into AWS bill | AWS native |
