The Trap Where Dependabot Wildcard Groups Disable Cooldown, and How to Deal with It

This page has been translated by machine translation. View original
Introduction
Suddenly, CI threw this error.
[ERR_PNPM_MINIMUM_RELEASE_AGE_VIOLATION] 1 lockfile entries failed verification:
  prettier-plugin-tailwindcss@0.8.1 was published at 2026-07-15T11:40:26.000Z,
  within the minimumReleaseAge cutoff (2026-07-15T01:45:56.100Z)
pnpm 11's supply chain defense feature minimumReleaseAge (default 24 hours) is blocking a freshly published package. But I should have set semver-patch-days: 3 in Dependabot's cooldown... so why was a PR created without waiting 3 days?
After investigating, I found that there is a pitfall in Dependabot's grouping settings.
The relationship between Dependabot cooldown and pnpm minimumReleaseAge
First, let's sort out the differences between these two mechanisms.
| Layer | Mechanism | Timing | Purpose |
|---|---|---|---|
| Dependabot cooldown | Delays PR creation | Before Dependabot opens a PR | Avoid updates right after unstable releases |
| pnpm minimumReleaseAge | Blocks at pnpm install time |
During installation in CI/local | Defense against supply chain attacks |
The two work independently. Even if Dependabot creates a PR, pnpm separately checks the package's publish date. Ideally, by aligning cooldown days >= minimumReleaseAge, the package will already be installable by the time Dependabot creates a PR. For details on minimumReleaseAge and problems with transitive dependencies, see "Dependabot CI fails because of pnpm v11's minimumReleaseAge".
Our project's settings:
cooldown:
  default-days: 7
  semver-major-days: 14
  semver-minor-days: 7
  semver-patch-days: 3
pnpm 11's default minimumReleaseAge is 1440 minutes (24 hours). With semver-patch-days: 3, it should easily be exceeded. So what happened?
The wildcard group trap
The problematic dependabot.yml setting:
groups:
  dependencies:
    patterns:
      - "*"
This setting bundles all dependencies into a single PR. It's tempting to add it to reduce review effort, but this was nullifying the cooldown.
Identifying the cause
Looking into the PR Dependabot created:
- PR title: "Bump the dependencies group in /frontend with 2 updates"
- Included packages:
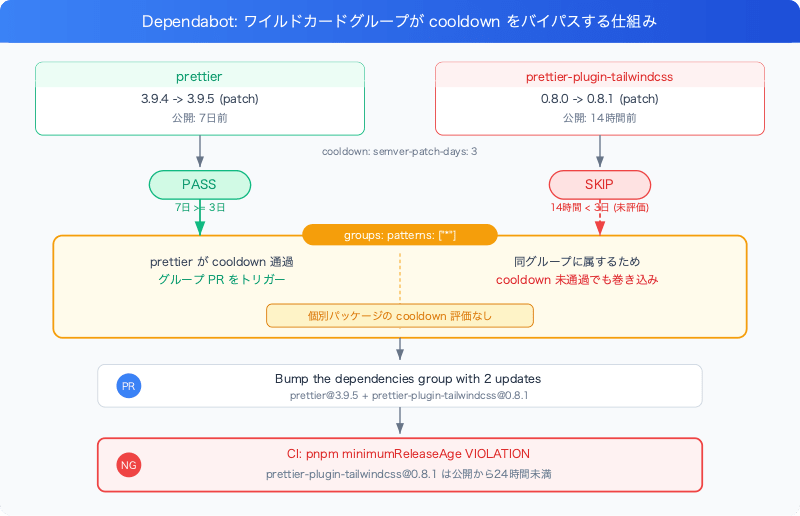
prettier3.9.4 → 3.9.5 (published: July 9, 7 days ago)prettier-plugin-tailwindcss0.8.0 → 0.8.1 (published: July 15, 14 hours ago)
prettier@3.9.5 was published 7 days ago and passes the semver-patch-days: 3 cooldown. The group update was triggered by this "eligible" package, and prettier-plugin-tailwindcss@0.8.1, which was still within the cooldown period, got swept in along with it.
Verification
# Check the publish date of prettier 3.9.5
curl -s "https://registry.npmjs.org/prettier" | \
  python3 -c "import sys,json; d=json.load(sys.stdin); print(d['time']['3.9.5'])"
# 2026-07-09T16:17:00.997Z  ← 7 days ago, passes cooldown
In other words, cooldown is not evaluated per package within a group. If even one package qualifies, the whole group is triggered.
Fix: Remove the wildcard group
The fix is simple. Remove the groups section.
updates:
 - package-ecosystem: "npm"
   directory: "/frontend"
   schedule:
     interval: "weekly"
   cooldown:
     default-days: 7
     semver-major-days: 14
     semver-minor-days: 7
     semver-patch-days: 3
-  groups:
-    dependencies:
-      patterns:
-        - "*"
Removing the group turns each package into its own PR, but since cooldown delays PR creation, the number of PRs doesn't actually increase that much.
Managing transitive deps with Dependabot
Frequently updated transitive deps like caniuse-lite cause the same problem. Previously I excluded them using pnpm's minimumReleaseAgeExclude, but excluding packages from the age check weakens supply chain defense.
A better approach:
- Add it explicitly to
package.jsonso it becomes managed by Dependabot - Since cooldown applies, updates right after publication are automatically delayed
minimumReleaseAgeExcludebecomes unnecessary
{
  "devDependencies": {
    "caniuse-lite": "^1.0.30001803"
  }
}
If knip (an unused dependency checker) reports it as an "unused dependency", add it to ignoreDependencies:
{
  "ignoreDependencies": ["caniuse-lite"]
}
Gaps in Dependabot coverage
During the investigation, I found another problem. knip was still at v5.88.1 and had not been updated to v6 (released in March 2026).
Cause: knip was in the root package.json, and Dependabot was only watching the /frontend directory.
# Only /frontend was targeted — the root was not covered
- package-ecosystem: "npm"
  directory: "/frontend"
Fix: Add an entry for the root directory.
# Root npm dependency updates
- package-ecosystem: "npm"
  directory: "/"
  schedule:
    interval: "weekly"
  cooldown:
    default-days: 7
    semver-major-days: 14
    semver-minor-days: 7
    semver-patch-days: 3
When using a pnpm workspace, devDeps in the root package.json (linters, formatters, etc.) are easy to overlook.
Changes from knip v5 → v6
While at it, I upgraded knip to v6. The main changes:
| Item | v5 | v6 |
|---|---|---|
| Parser | TypeScript | oxc-parser + oxc-resolver |
| Speed | - | Significantly faster |
| Node.js requirement | v18+ | v20.19.0+ |
| Plugin detection | - | Improved detection of PostCSS, etc. |
In v6, PostCSS plugin detection has improved, so I was able to remove postcss from ignoreDependencies. On the other hand, detection of system binaries in scripts (ssh-keygen, lsof, etc.) also improved, so I had to add them to ignoreBinaries.
Summary
| Problem | Root cause | Fix |
|---|---|---|
| minimumReleaseAge violation | Group bypassed cooldown | Remove the wildcard group |
| Overuse of minimumReleaseAgeExclude | Transitive deps not managed by Dependabot | Promote to explicit devDep |
| knip not updated for 4 months | Root package.json not covered by Dependabot | Add directory: "/" |
Points to note when grouping with Dependabot:
- A wildcard
*group makes cooldown meaningless - If you use groups, split them into meaningful units (React-related, testing-related, etc.)
- Or, don't use groups and let cooldown control PR frequency
To properly coordinate Dependabot cooldown and pnpm minimumReleaseAge, it's important to understand both layers and verify that grouping doesn't break them.