AWS Provider に aws_devopsagent_agent_space が追加されたので、AWS DevOps Agent の Agent Space を Terraform で作ってみた

AWS Provider v6.69.0(2026-10-14 リリース)で、AWS DevOps Agent の Agent Space を作る aws_devopsagent_agent_space が追加されました。
ただし、Association(AWS アカウントの関連付け)などの他のリソースは aws プロバイダーに無く、引き続き awscc プロバイダーが必要です。
そこで、aws で Agent Space と IAM ロールを作り、awscc で Association を付ける構成を試してみました。
awscc だけで構築する手順は、次の公式ガイドと過去記事にあります。
公式ガイドは、awscc で Agent Space、Association、Asset などを作る手順です。
過去記事は、awscc だけで Agent Space と Association を作った記事です。
検証環境は次のとおりです。
- Terraform v1.16.6
hashicorp/awsv6.69.1hashicorp/awsccv1.106.0hashicorp/timev0.14.2- リージョン: ap-northeast-1(東京)
aws と awscc の対応範囲
aws プロバイダーにある DevOps Agent のリソースは、aws_devopsagent_agent_space だけです(2026-10-16 に確認)。
| リソース | aws | awscc |
|---|---|---|
| AgentSpace | ○(v6.69.0 から) | ○ |
| Association | × | ○ |
| Service | × | ○ |
| PrivateConnection | × | ○ |
| Trigger | × | ○ |
| Asset | × | ○ |
Asset と PrivateConnection は、aws への追加 PR が出ています。2026-10-20 時点で、どちらも open です。
aws と awscc で Agent Space と Association を作る
Agent Space と IAM ロールを aws プロバイダーで、Association を awscc プロバイダーで作ります。
data "aws_caller_identity" "current" {}
data "aws_region" "current" {}

# IAM ロールの反映を待ってから Agent Space と Association を作る
resource "time_sleep" "wait_for_iam_propagation" {
  depends_on      = [aws_iam_role.agent_space, aws_iam_role_policy_attachment.agent_space]
  create_duration = "30s"
}

resource "aws_devopsagent_agent_space" "this" {
  name        = "tf-aws-provider-space-sample"
  description = "Agent Space created by the aws provider"

  depends_on = [time_sleep.wait_for_iam_propagation]
}

data "aws_iam_policy_document" "agent_space_trust" {
  statement {
    effect  = "Allow"
    actions = ["sts:AssumeRole"]

    principals {
      type        = "Service"
      identifiers = ["aidevops.amazonaws.com"]
    }

    condition {
      test     = "StringEquals"
      variable = "aws:SourceAccount"
      values   = [data.aws_caller_identity.current.account_id]
    }

    condition {
      test     = "ArnLike"
      variable = "aws:SourceArn"
      values   = ["arn:aws:aidevops:${data.aws_region.current.region}:${data.aws_caller_identity.current.account_id}:agentspace/*"]
    }
  }
}

resource "aws_iam_role" "agent_space" {
  name               = "DevOpsAgentRole-AgentSpace-tfsample"
  assume_role_policy = data.aws_iam_policy_document.agent_space_trust.json
}

resource "aws_iam_role_policy_attachment" "agent_space" {
  role       = aws_iam_role.agent_space.name
  policy_arn = "arn:aws:iam::aws:policy/AIDevOpsAgentAccessPolicy"
}

resource "awscc_devopsagent_association" "monitor" {
  agent_space_id = aws_devopsagent_agent_space.this.agent_space_id
  service_id     = "aws"

  configuration = {
    aws = {
      account_id         = data.aws_caller_identity.current.account_id
      account_type       = "monitor"
      assumable_role_arn = aws_iam_role.agent_space.arn
    }
  }

  depends_on = [aws_devopsagent_agent_space.this]
}
terraform {
  required_version = "~> 1.16"

  required_providers {
    aws = {
      source  = "hashicorp/aws"
      version = "~> 6.69"
    }
    time = {
      source  = "hashicorp/time"
      version = "~> 0.13"
    }
    awscc = {
      source  = "hashicorp/awscc"
      version = "~> 1.0"
    }
  }
}

provider "aws" {
  region = "ap-northeast-1"
}

provider "awscc" {
  region = "ap-northeast-1"
}
time_sleep を入れた理由
time_sleep を入れずに、IAM ロールの作成から数秒後に Association の作成を始めると、1 回目の apply が次のエラーで失敗しました。
╷
│ Error: AWS SDK Go Service Operation Incomplete
│
│   with awscc_devopsagent_association.monitor,
│   ...
│
│ Waiting for Cloud Control API service CreateResource operation completion returned: waiter state transitioned to FAILED. StatusMessage: Error occurred during operation 'AWS::DevOpsAgent::Association: Invalid STS role configuration for session monitorVerificationAssociationRoleSession. Verify the role's trust policy. (Service: DevOpsAgent, Status Code: 400,
│ Request ID: <REQUEST_ID>) (SDK Attempt Count: 1)'.. ErrorCode: GeneralServiceException
原因は、IAM ロールの作成直後に Association の作成が始まったことだと考えています。
確認のため、time_sleep なしで IAM ロールと Agent Space の片方だけを先に作り、180 秒待ってから残りを apply しました(各 2 回)。
IAM ロールを先に作ると成功し、Agent Space を先に作ると失敗しました。
そこで、公式サンプルと同じ位置に time_sleep(30 秒)を入れました。
サンプルでは IAM ロールと Agent Space の間に置いています。
Association は Agent Space の作成後に始まるので、Association の前にも同じ待ちが入ります。
aws_devopsagent_agent_space では Operator App を設定できない
現時点では、aws_devopsagent_agent_space には Operator App(認証方式と Operator App 用の IAM ロール)を設定する引数がありません。
CLI かコンソールで別途、Operator App 用の IAM ロールを Agent Space に割り当てる必要があります。
割り当てない状態で、Web アプリを起動しようとすると次のエラーで失敗します。
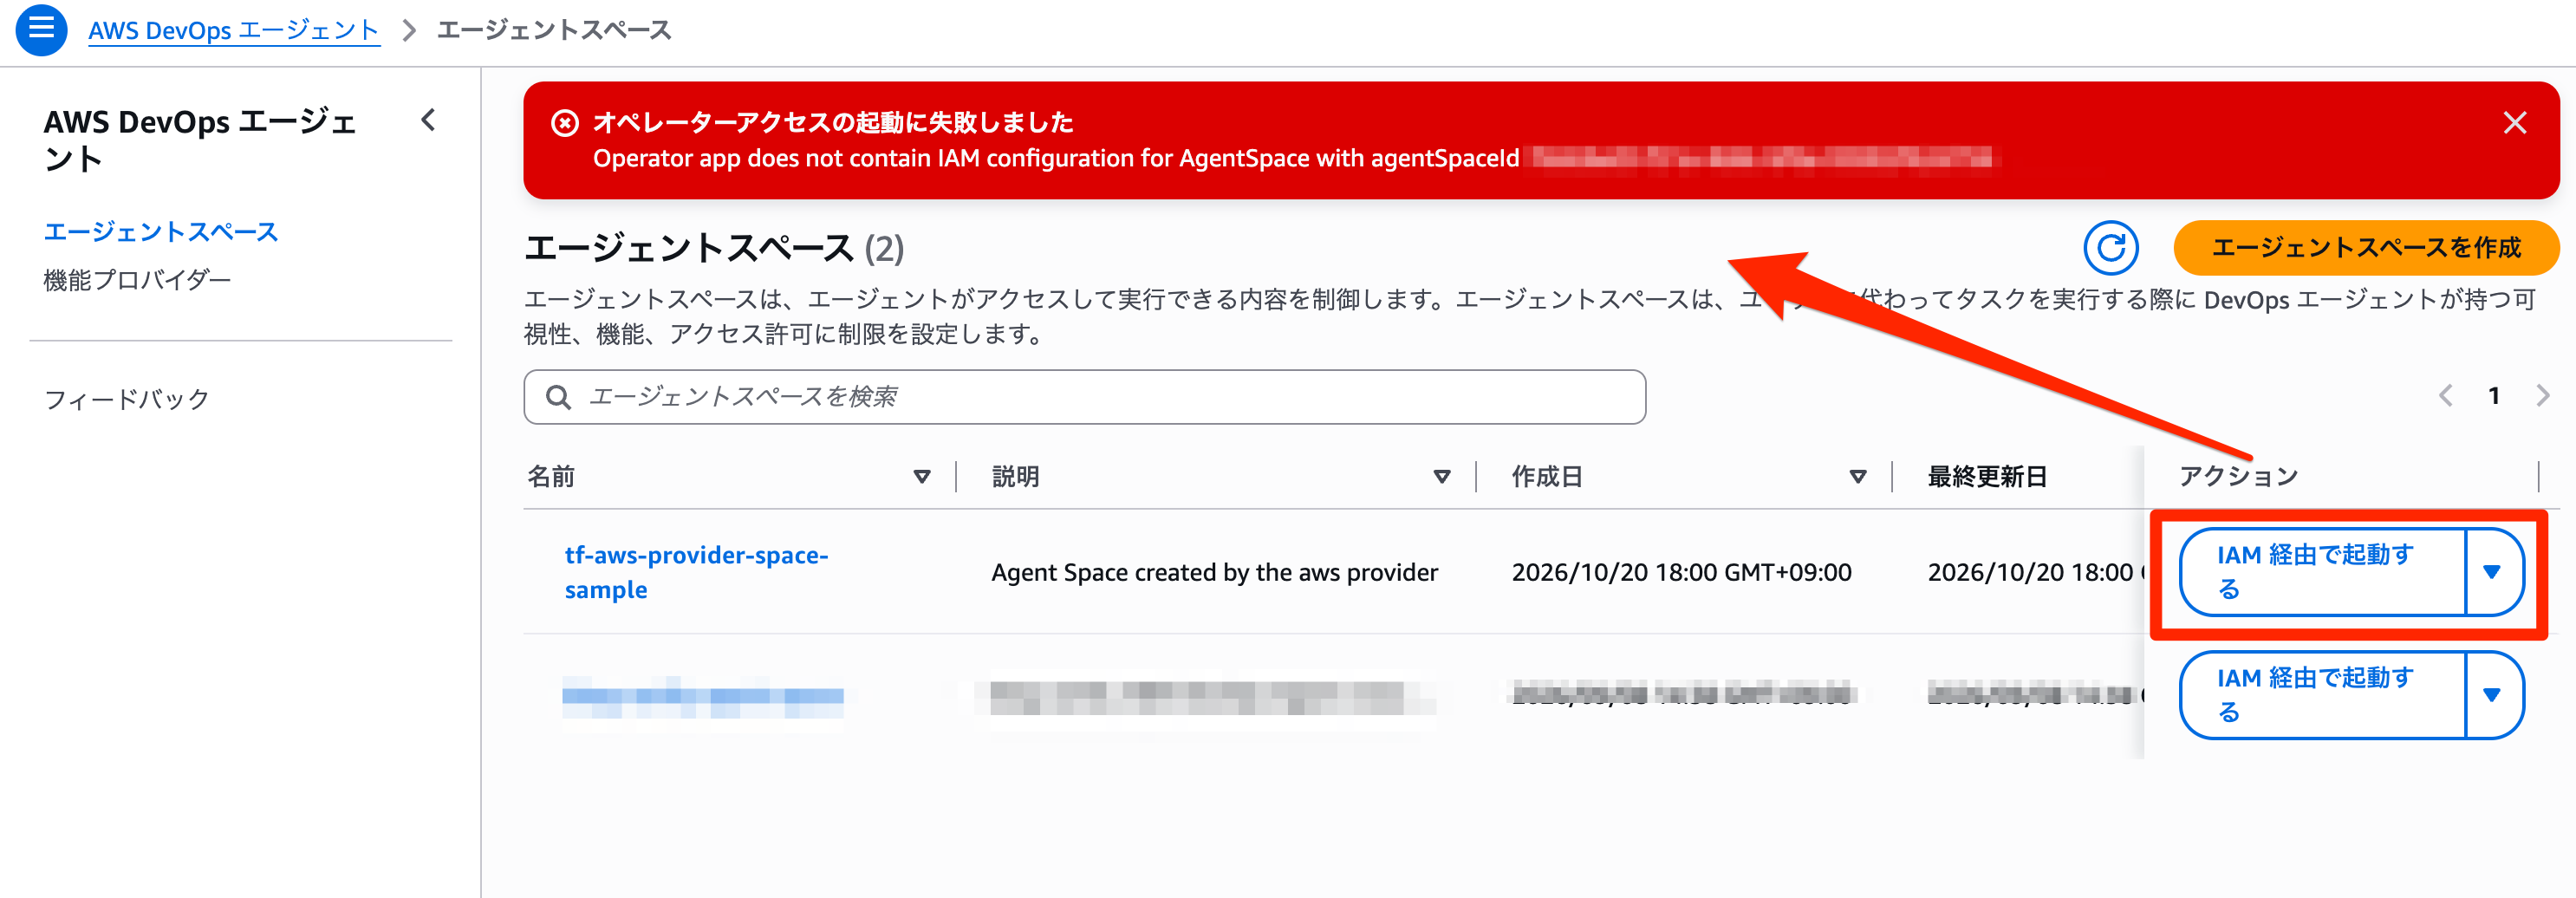
オペレーターアクセスの起動に失敗しました
Operator app does not contain IAM configuration for AgentSpace with agentSpaceId <AGENT_SPACE_ID>
ちなみに、awscc_devopsagent_agent_space には operator_app があるので、Terraform で設定可能です。
# Operator App 用の IAM ロール(aws_iam_role.operator)の定義は省略
resource "awscc_devopsagent_agent_space" "this" {
  name        = "tf-awscc-provider-space"
  description = "Agent Space created by the awscc provider"

  operator_app = {
    iam = {
      operator_app_role_arn = aws_iam_role.operator.arn
    }
  }

  depends_on = [aws_iam_role_policy_attachment.operator]
}
おわりに
現時点では Association などが aws プロバイダーに無いため、awscc との併用が必要です。
今後のアップデートでawsプロバイダー単体で設定が完結するようになることを期待しています。