クロスリージョンの TGW ピアリングと VPC ピアリングで Multipath Resilience を有効化してみた

はじめに
2026年11月17日に、クロスリージョン通信に 99.999% の可用性 SLA を付ける Multipath Resilience が発表されました。
Multipath Resilience を有効にすると、各パケットのコピーが物理的に分離された複数の経路へ送られ、宛先リージョンでは最初に届いたパケットが渡され、後から届いた重複は破棄されます。
この記事では、N. Virginia(us-east-1)と Oregon(us-west-2)の間の Transit Gateway(TGW)ピアリング attachment と VPC ピアリングで、Multipath Resilience の有効化を試しました。
検証環境
- AWS CLI:2.41.0
- リージョン:us-east-1(requester 側)、us-west-2(accepter 側)
- アカウント:requester 側と accepter 側で同一
TGW ピアリング attachment
us-east-1 と us-west-2 に TGW を1つずつ作成した状態から始めます。attachment の requester は us-east-1、accepter は us-west-2 です。
有効化前の状態
options を指定せずに作成して accept した attachment を describe すると、Options に Multipath Resilience の項目が出ます。
aws ec2 describe-transit-gateway-peering-attachments --region us-east-1 --transit-gateway-attachment-ids tgw-attach-0123456789abcdef0
"Options": {
    "RequesterAllowMultipathResilience": false,
    "AccepterAllowMultipathResilience": false,
    "MultipathResilienceStatus": "disabled"
}
options なしで実行した create の応答と accept の応答には、Multipath Resilience の項目が出ませんでした。accept 応答の Options は DynamicRouting のみでした。
既存の attachment で有効化する
modify-transit-gateway-peering-attachment を requester 側(us-east-1)、accepter 側(us-west-2)の順に実行します。まず requester 側です。
aws ec2 modify-transit-gateway-peering-attachment --region us-east-1 --transit-gateway-attachment-id tgw-attach-0123456789abcdef0 --options AllowMultipathResilience=true
応答の Options は次のとおりです。指定したのは AllowMultipathResilience=true だけですが、RequesterMultipathResilienceMode には always-on が入りました。
"Options": {
    "RequesterAllowMultipathResilience": true,
    "RequesterMultipathResilienceMode": "always-on",
    "AccepterAllowMultipathResilience": false,
    "MultipathResilienceStatus": "pending"
}
この時点では、どちらのリージョンから describe しても MultipathResilienceStatus は pending でした。続けて accepter 側です。
aws ec2 modify-transit-gateway-peering-attachment --region us-west-2 --transit-gateway-attachment-id tgw-attach-0123456789abcdef0 --options AllowMultipathResilience=true
この modify の応答でも MultipathResilienceStatus は pending でした。約14秒後の describe では enabled になっていました。
aws ec2 describe-transit-gateway-peering-attachments --region us-east-1 --transit-gateway-attachment-ids tgw-attach-0123456789abcdef0 --query TransitGatewayPeeringAttachments\[0\].\[State\,Options\]
[
    "available",
    {
        "RequesterAllowMultipathResilience": true,
        "RequesterMultipathResilienceMode": "always-on",
        "AccepterAllowMultipathResilience": true,
        "AccepterMultipathResilienceMode": "always-on",
        "MultipathResilienceStatus": "enabled"
    }
]
既存の attachment を modify で有効化している間、State は available のままです。切り替わりを示すのは MultipathResilienceStatus だけです。
作成時に有効化する
create-transit-gateway-peering-attachment の options に AllowMultipathResilience=true を指定します。
aws ec2 create-transit-gateway-peering-attachment --region us-east-1 --transit-gateway-id tgw-0123456789abcdef0 --peer-transit-gateway-id tgw-0fedcba9876543210 --peer-account-id 111122223333 --peer-region us-west-2 --options AllowMultipathResilience=true
"Options": {
    "RequesterAllowMultipathResilience": true,
    "RequesterMultipathResilienceMode": "always-on",
    "AccepterAllowMultipathResilience": false,
    "MultipathResilienceStatus": "pending"
}
同一アカウントの接続では、accepter 側で modify を実行せず accept しただけで、AccepterAllowMultipathResilience が true、MultipathResilienceStatus が enabled になりました。
accept から requester 側で available と enabled を確認するまでは約3分23秒でした。options なしの attachment は約3分15秒で、10〜15秒間隔の確認では差を読み取れませんでした。
Console での表示
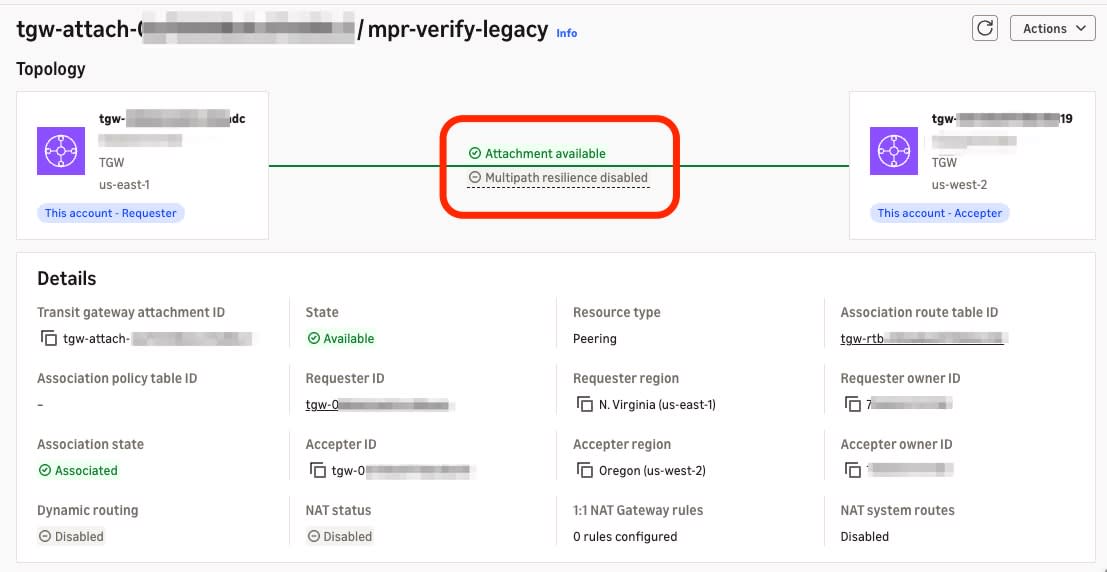
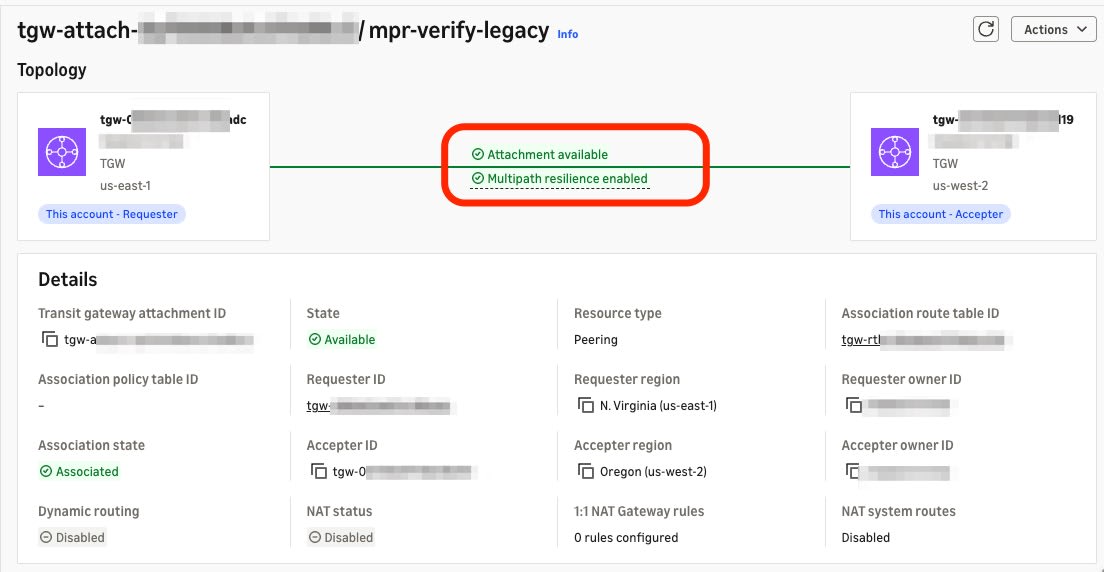
attachment 詳細のトポロジー図で、Attachment available の下の表示が Multipath resilience disabled から enabled に変わります。画像は requester 側(us-east-1)の画面です。State や Dynamic routing など詳細欄の項目は有効化の前後で同じです。
VPC ピアリング
us-east-1 と us-west-2 に VPC を1つずつ新規に作り、その間にピアリング接続を作成しました。requester は us-east-1、accepter は us-west-2 です。
既存の接続で有効化する
options を指定せずに作成して accept した接続(Status は active)で有効化します。有効化前と両側の許可後で describe の結果を比べると、次の項目が変わりました。
| 項目 | 有効化前 | 両側許可後 |
|---|---|---|
| MultipathResilienceStatus | disabled | enabled |
| requester 側の AllowMultipathResilience | false | true |
| accepter 側の AllowMultipathResilience | false | true |
| MultipathResilienceMode | 項目なし | always-on |
requester 側は --requester-peering-connection-options で指定します。accepter 側は --accepter-peering-connection-options で指定します。
aws ec2 modify-vpc-peering-connection-options --region us-east-1 --vpc-peering-connection-id pcx-0123456789abcdef0 --requester-peering-connection-options AllowMultipathResilience=true
aws ec2 modify-vpc-peering-connection-options --region us-west-2 --vpc-peering-connection-id pcx-0123456789abcdef0 --accepter-peering-connection-options AllowMultipathResilience=true
requester 側だけが許可した状態では、どちらのリージョンから describe しても MultipathResilienceStatus は pending でした。accepter 側の modify の約11秒後に describe した結果は次のとおりです。
aws ec2 describe-vpc-peering-connections --region us-east-1 --vpc-peering-connection-ids pcx-0123456789abcdef0 --query VpcPeeringConnections\[0\].\[Status.Code\,MultipathResilienceStatus\,RequesterVpcInfo.PeeringOptions\,AccepterVpcInfo.PeeringOptions\]
[
    "active",
    "enabled",
    {
        "AllowDnsResolutionFromRemoteVpc": false,
        "AllowEgressFromLocalClassicLinkToRemoteVpc": false,
        "AllowEgressFromLocalVpcToRemoteClassicLink": false,
        "AllowMultipathResilience": true,
        "MultipathResilienceMode": "always-on"
    },
    {
        "AllowDnsResolutionFromRemoteVpc": false,
        "AllowEgressFromLocalClassicLinkToRemoteVpc": false,
        "AllowEgressFromLocalVpcToRemoteClassicLink": false,
        "AllowMultipathResilience": true,
        "MultipathResilienceMode": "always-on"
    }
]
接続の状態を示す Status.Code は、有効化の前後とも active です。
作成時に有効化する
create-vpc-peering-connection の --requester-peering-connection-options に、AllowMultipathResilience=true を指定します。
aws ec2 create-vpc-peering-connection --region us-east-1 --vpc-id vpc-0123456789abcdef0 --peer-vpc-id vpc-0fedcba9876543210 --peer-region us-west-2 --requester-peering-connection-options AllowMultipathResilience=true
create の応答の MultipathResilienceStatus は pending です。同一アカウントの接続では、accepter 側で modify を実行せずに accept しただけで、その応答の時点で accepter 側の AllowMultipathResilience が true になっていました。MultipathResilienceStatus も enabled になっていました。
aws ec2 accept-vpc-peering-connection --region us-west-2 --vpc-peering-connection-id pcx-0abcdef0123456789 --query VpcPeeringConnection.\[Status.Code\,MultipathResilienceStatus\,AccepterVpcInfo.PeeringOptions\]
[
    "provisioning",
    "enabled",
    {
        "AllowDnsResolutionFromRemoteVpc": false,
        "AllowEgressFromLocalClassicLinkToRemoteVpc": false,
        "AllowEgressFromLocalVpcToRemoteClassicLink": false,
        "AllowMultipathResilience": true,
        "MultipathResilienceMode": "always-on"
    }
]
この応答の時点では Status.Code が provisioning で、accept の約11秒後の describe で active になっていました。
TGW ピアリングとの API の違い
TGW ピアリングと VPC ピアリングでは、応答に含まれる項目の位置と、modify で使う引数が異なります。
| TGW ピアリング attachment | VPC ピアリング | |
|---|---|---|
| MultipathResilienceStatus | Options の中 | 接続の最上位 |
| 許可フラグ | Options の中 | 各側の PeeringOptions の中 |
| modify の引数 | --options |
--requester-peering-connection-options、--accepter-peering-connection-options |
| modify の応答の MultipathResilienceStatus | あり(pending) | なし |
| accept の応答の MultipathResilienceStatus | なし | あり |
対応範囲と SLA
対象は、クロスリージョンの VPC ピアリング、TGW ピアリング attachment、Cloud WAN の通信です。使えるリージョンは N. Virginia、Ohio、N. California、Oregon、Ireland です。
SLA は、AWS バックボーンの部分について、Network Path(片方向の通信)ごとに Qualifying Minute を対象に測定されます。Qualifying Minute は、1分あたり 250,000 パケット以上で、かつ 1 Gbps を超えるフロー(5-tuple)を含まない分です。
料金
有効化した接続から別リージョンへ送信したデータに、GB 単位の料金がかかります。この料金は、リージョン間データ転送料金に上乗せして請求されます。受信したデータには Multipath Resilience の料金がかかりません。VPC の料金ページの表では、単価は次の2通りです。
- N. Virginia と Ohio の間:$0.015/GB
- そのほかのリージョンの組み合わせ(us-east-1 と us-west-2 の間を含む):$0.03/GB
TGW ピアリングでは、Multipath Resilience の料金に加えて、TGW の料金もかかります。
- TGW ピアリング attachment の時間料金:$0.05/時。ピアリングした両側の TGW の所有者それぞれに請求されます
- TGW のデータ処理料金:$0.02/GB。VPC から TGW へ送ったデータに課金されます
まとめ
Multipath Resilience が、北米4リージョンとアイルランドで利用可能になりました。
AWS Transit Gateway の SLA は、月間の稼働率で、複数 AZ に配置した TGW が 99.99%、それ以外が 99.9% です。Multipath Resilience を有効にしたクロスリージョンの TGW ピアリング接続は、日次の稼働率 99.999% の SLA で利用できます。TGW などのネットワーク接続に、より高い可用性と信頼性が求められる場合の選択肢が増えました。
Multipath Resilience の利用には、送信データに対して $0.03/GB(N. Virginia と Ohio の間のみ $0.015/GB)の料金がかかります。対象リージョンで、この料金に見合う可用性が必要な場合に、導入を検討してください。
GA 時点では東京リージョンが対象外でしたが、Multipath Resilience のサポートリージョンに加わるのを待ちたいと思います。